
The Arcadia exploit wasn’t just a $3.6 million bug. It was a two-day, multi-phase takedown that turned the protocol’s own defenses into weapons. Circuit breakers became blindfolds. Flashloans became cloaks. And a single unchecked router call punched straight through the Rebalancer contract’s core logic.
This wasn’t a novel vulnerability. It was an architectural oversight; missed not just by Arcadia Finance, but by four different audit firms. The root cause was a lack of input validation, embedded in a high-privilege function, that assumed external routers were safe by default.
In an ecosystem obsessed with zero-days and reentrancy, the Arcadia exploit is a reminder: most losses come from old failures wearing new disguises.
This postmortem dissects exactly how the Arcadia exploit unfolded, why audits failed to catch it, and what design decisions put the protocol in the blast radius. Builders, this one’s for you.
The Arcadia exploit executed at 4:05 AM UTC on July 15, 2025, targeting Arcadia Finance’s Rebalancer contract on the Base blockchain. Within minutes, $3.6 million worth of USDC and USDS were drained, swapped into WETH, and bridged to Ethereum through fresh intermediary addresses to obfuscate the trail.
Despite Arcadia’s built-in circuit breakers — designed to halt suspicious behavior — the exploit ran uninterrupted. Why? Because the attacker had pre-triggered the circuit breaker 20 hours earlier, baiting the team into unpausing the protocol. This unpause activated a cooldown period, rendering the protocol unable to pause again when the real exploit began.
Here’s the full attack window:
The Arcadia exploit wasn’t a smash-and-grab. It was a surgical, two-day operation exploiting flawed assumptions in both code and system design.
The Arcadia exploit didn’t start with an attack. It started with a setup.
On July 14 at 9:22 AM UTC, the attacker deployed malicious contracts that intentionally tripped Arcadia’s circuit breakers. The protocol correctly paused within seconds, exactly as designed.
But the attacker knew Arcadia’s safety logic better than Arcadia did. After four hours of internal review, the Arcadia team deemed the contracts non-malicious and unpaused the system. This seemingly harmless action triggered a cooldown period, a governance safeguard that prevented the protocol from pausing again for several hours.
This cooldown wasn’t a bug. It was a design feature. But on July 15, it became a liability.
At 4:05 AM UTC on July 15, with the cooldown still active, the real attack began:
No reentrancy. No price oracle games. Just a complete failure of input validation and privilege separation, wrapped inside a rigged cooldown window.
At the heart of the Arcadia exploit was a single unforced error: the swapViaRouter() function blindly trusted that any router address passed to it would be safe.
That assumption was fatal.
The attacker injected their own contract as the router inside a call to rebalance(). This contract inherited Rebalancer privileges and executed arbitrary logic under the protocol’s full trust. No validation, no whitelisting, no guardrails.
The unchecked path:
Rebalancer.rebalance()
→ AccountV1.flashAction()
→ actionTarget.executeAction()
→ _swap()
→ swapViaRouter()
→ router.call(data)
This is textbook privilege escalation: a low-trust input (router address) ends up controlling a high-privilege function. Once swapViaRouter handed off execution, it was game over.
The cooldown period (intended to prevent governance attacks) created a 20-hour window where circuit breakers couldn’t function. The attacker gamed it by intentionally triggering a false positive the day before.
By the time the real exploit began, Arcadia’s only line of defense was disabled by design.
The Rebalancer contract, where the Arcadia exploit originated, was excluded from scope in three of four audits. The one firm that reviewed it flagged a similar pattern — but dismissed the risk without modeling this exact call path.
When validation assumptions go unchecked and scope is siloed, attackers win.
Olympix static analysis flagged the final choke point of the Arcadia exploit: a high-privilege call() to an unvalidated router address with unchecked payload data. This is where the exploit converged — and where most tools, audits included, historically fail to catch cascading privilege flows.
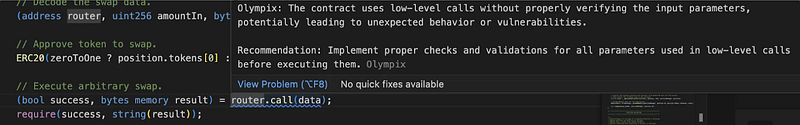
But static analysis alone only lit up the tail end. The full path to exploitation required deeper, context-aware analysis. That’s where Olympix tooling went further; surfacing interconnected risk patterns across the Rebalancer contract:
In isolation, each of these issues might appear benign. Together, they formed the exact shape of a protocol-level privilege escalation.
Olympix would have caught this; not by guessing the attacker’s payload, but by structurally invalidating the trust model that enabled it. That’s what modern security tooling is supposed to do.
Uncover vulnerabilities early with Olympix’ free static analyzer. Trusted by over 30% of Solidity developers. Easy to use. Proven. Ready for your code. Get started for FREE!
Never trust an external address in a high-privilege context without strict validation. The Arcadia exploit weaponized a router field meant for DEX calls — but no check ensured the router was actually a DEX.
Lesson: Always whitelist critical addresses. If that’s infeasible, enforce interface checks, revert on unknown selectors, and log address changes with circuit-breaker triggers.
The attacker’s router contract inherited the full privileges of the Rebalancer simply by being passed into call(). This broke the implicit trust model and allowed access control to collapse.
Lesson: Never delegate execution without explicit capability scoping. If a contract is calling into another, ensure only low-privilege actions are possible; even in success paths.
Arcadia’s circuit breaker cooldown, designed as a defense, became a liability. The attacker pre-triggered the defense to ensure it couldn’t activate when needed.
Lesson: If a system can only detect after a threat begins, ensure it can re-engage defenses at any time. Add override paths. Don’t hard-code blind spots.
Three audits never looked at the vulnerable contract. The one that did, underestimated the path to exploitability. Even comprehensive audits aren’t immune to blind spots.
Lesson: Use audits as validation, not detection. Pair them with continuous analysis and scoped tooling that doesn’t rely on human prioritization to surface critical logic flaws.
The Arcadia exploit ran for 20 minutes before any team response. A real-time alerting system could have stopped the attack by minute two. That’s a $3.6M difference.
Lesson: Detection speed is security. Monitoring isn’t optional — it’s the last line of defense before capital loss.
4. Bake Security Into the Dev Cycle
The Arcadia exploit didn’t require exotic tooling or undiscovered opcodes. It required a series of old, fixable mistakes:
This was preventable. And that’s what makes it dangerous.
Every protocol with flashloan exposure, router delegation, or pause-based protections is at risk if they haven’t modeled these patterns end-to-end. The next $3.6M loss won’t look like Arcadia, but it’ll rhyme.
Builders, don’t wait for the audit to catch what your test suite and tooling should’ve surfaced weeks ago. Design like you’re being targeted. Because you are.
Arcadia Finance exploited, $3.5M stolen and converted to WETH
Lessons from Arcadia Finance exploit and how real-time alerts could have saved $3.5M
How Arcadia Finance lost $3.5m due to Lack of Input Validation
Olympix provides advanced Solidity analysis tools to help developers identify and fix vulnerabilities before they become critical exploits.
Get started today to fortify your smart contracts and proactively shield them from exploits in the evolving Web3 security landscape.
Connect with us on:
Twitter | LinkedIn | Discord | Medium | Instagram | Telegram | Newsletter