
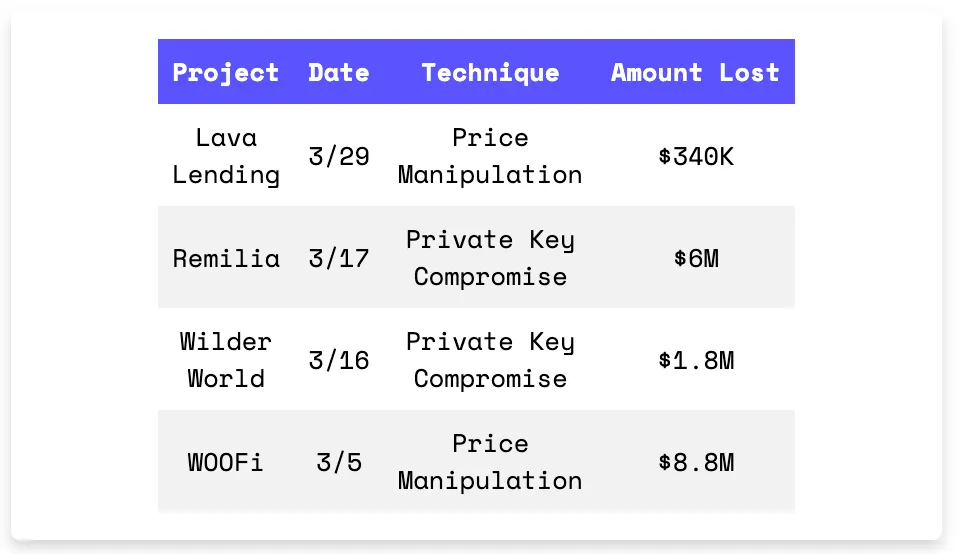
WOOFi lost $8.8M in a classic low-liquidity price manipulation. Wilder World and Remilia were hit by private key compromises totaling $7.8M. Lava Lending fell to a flash-loan driven LPT inflation attack. Four very different protocols, same theme: insecure trust assumptions.
On March 29th, the Lava Lending exploit on the Arbitrum chain resulted in a $340K loss. The attacker initially borrowed ETH, USDC, and USDC.e flash loans from Balancer, Uniswap, and Aave. Subsequently, the attacker traded LPT tokens, with each transaction incurring a trading fee. This strategy reduced the liquidity of LPT tokens, artificially inflating their price and enabling the attacker to make profits.

Exploit Contract (on Arbitrum chain): 0x10bdA01aC4E644fD84a04Dab01E15A5eDcEE46dD
Transaction Hash: 0xcb1a2f5eeb1a767ea5ccbc3665351fadc1af135d12a38c504f8f6eb997e9e603
On March 17th, the Remilia exploit on the Ethereum Mainnet resulted in a $6M loss. The root cause of the exploit was that the exploiter got unauthorized access to Remilia’s BitWarden account. Despite the multisig initially requiring 4 signers, the attacker had access to more than 4 private keys, enabling them to drain 300 ETH and assets valued at 544 ETH, which included REMIO and MILADY NFTs.

Exploit Contract: 0xB520F068a908A1782a543aAcC3847ADB77A04778
Transaction Hash: 0x412c15ff396374f866d8a43421bba20f687c4ee3c90c7b55eefaa105feb3e10f
On March 16th, the Wilder World exploit on the Ethereum Mainnet resulted in a $1.8M loss. The root cause of the exploit was the compromise of one of Wilder World’s private keys, enabling the attacker to transfer ownership of 9 legacy vault contracts. The attacker drained 515 ETH worth of WILD and MEOW tokens. The Wilder World team acknowledged the incident and requested that the exploiter return the funds.

Exploit Contract: 0x37358Aa5D051B434C23Bad744E56E6A484107272
Transaction Hash: 0x649e73c18f6f578620f70b82b45bd9591a39a8a408029ca48f4ab4c41ba75650
On March 5th, the WOOFi exploit on the Arbitrum chain resulted in a $8.8M loss. The root cause of the exploit was WOO token’s low liquidity, enabling the attacker to manipulate its price. Initially borrowing 7.7M WOO tokens and depositing them into WOOFi’s liquidity pool, the attacker artificially inflated the WOO token price, profiting after repaying the loans. The WOOFi team acknowledged the incident and proposed a 10% bounty reward to the exploiter.
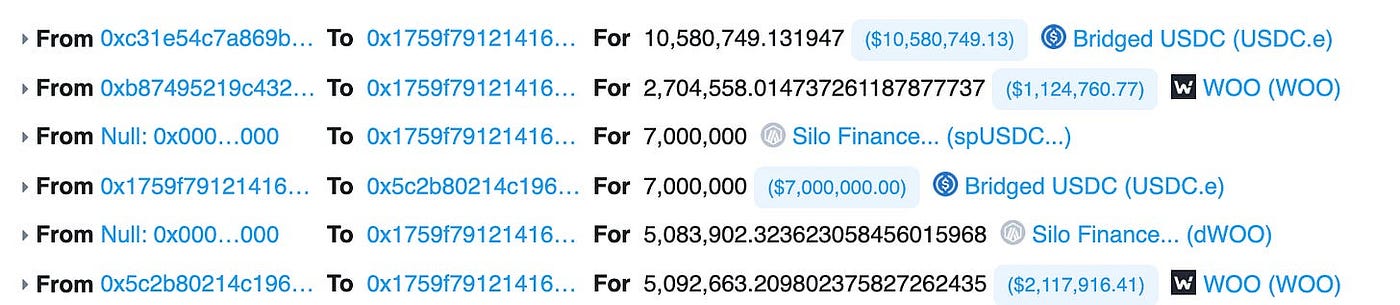
Exploit Contract (on Arbitrum chain): 0xeff23b4be1091b53205e35f3afcd9c7182bf3062
Transaction Hash: 0x57e555328b7def90e1fc2a0f7aa6df8d601a8f15803800a5aaf0a20382f21fbd