
Edel Finance's $403K Loss and How Olympix Would Have Prevented It
Date: July 1, 2026 (00:24 UTC), Ethereum block 25434062
Chain: Ethereum mainnet
Loss: approximately $403K in protocol bad debt
Class: collateral priced from a flash-loan-manipulable spot rate
Status: in scope for pre-deployment analysis, preventable
Summary
On July 1, 2026, Edel Finance was left with roughly $403K in bad debt after an attacker inflated the value of collateral and borrowed against it. Edel is a lending platform for tokenized equities, and it valued wGOOGLx collateral using the wrapped xStocks exchange rate between wGOOGLx and GOOGLx. That rate was read as a live spot value with no time-weighting and no manipulation guard, which meant the number the lending market trusted was a number an attacker could move. Using a 180,000 USDC flash loan from Morpho, the attacker distorted that rate inside a single transaction until wGOOGLx appeared to be worth roughly 78 times its true value, borrowed far more than the collateral could support, and left the protocol holding the shortfall. The proceeds were consolidated into 224 ETH and sent through Tornado Cash. No key was stolen and no admin function was abused. The lending market did exactly what its code told it to do, using a price that was never safe to trust.
Background
A lending market's entire safety model rests on one question: what is the collateral worth. Every borrowing limit, every liquidation threshold, and every solvency guarantee is downstream of that answer. If the price feeding those calculations can be moved by the same person doing the borrowing, the collateralization requirement stops being a constraint and becomes a formality.
This is why manipulation-resistant pricing exists. A time-weighted average price, an oracle with multiple independent sources, or a redemption rate that can't be moved within a block all serve the same purpose: they make the value a lending market believes expensive or impossible for a borrower to influence in the moment they borrow.
Edel priced wGOOGLx collateral off a live wrapped xStocks exchange rate instead. The rate reflected the state of the wrapper at the instant it was read, so a borrower who could change that state could change what their collateral was worth.
Root Cause
The flaw was that collateral valuation depended on a spot read of the wGOOGLx to GOOGLx exchange rate, with no time-weighted average and no manipulation resistance of any kind.
Because the rate was derived from live wrapper state rather than a smoothed or independently sourced feed, it could be moved within a single transaction. An attacker holding temporary capital could distort the rate, take the inflated valuation, and act on it before anything reverted. The lending market read the manipulated number, treated it as the honest value of the collateral, and extended credit accordingly.
The flash loan was the funding mechanism, not the vulnerability. It gave the attacker temporary size, roughly 180,000 USDC borrowed and repaid inside the same transaction, but the reason that size translated into $403K of bad debt is that the price feed could be moved at all. A market that valued the same collateral through a manipulation-resistant source would've seen no meaningful change from the attacker's activity and would've extended credit against the real value.
Attack Flow
- The attacker opened a flash loan of 180,000 USDC from Morpho, providing temporary capital with no upfront funds at risk beyond gas.
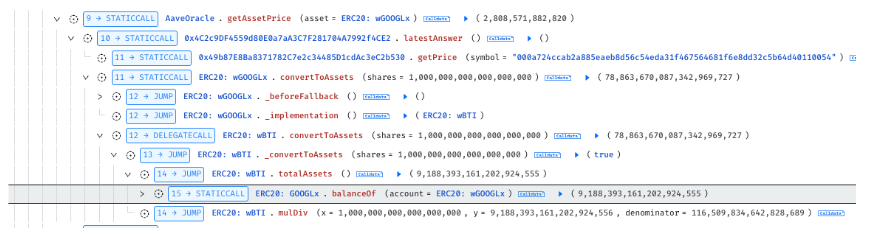
- Within that transaction, they manipulated the wrapped xStocks exchange rate between wGOOGLx and GOOGLx, the rate Edel's markets used to value wGOOGLx collateral.
- The manipulation drove the apparent value of wGOOGLx to roughly 78 times its correct value.
- Against that inflated valuation, the attacker borrowed from Edel's lending markets, extracting far more than the collateral was genuinely worth.
- The flash loan was repaid within the same transaction, the extracted value was consolidated into 224 ETH, and the proceeds were sent through Tornado Cash.
Impact
Edel was left with approximately $403K in bad debt, borrowings backed by collateral that never had the value the protocol credited it with. Bad debt in a lending market is a loss carried by the protocol and its lenders rather than by the borrower, and it doesn't resolve on its own. The wGOOGLx market was left insolvent by the difference between what was borrowed and what the collateral is actually worth.
The Problem With Audit-Only Security
A price-feed flaw is one of the clearest illustrations of why point-in-time review isn't a security model, because the vulnerability isn't a broken line of code. It's a broken assumption about what the code is allowed to trust.
Reviewers see getPrice() or an exchange-rate read and the call itself is correct. It returns a real number, computed from real state, with no arithmetic error and no missing access check. Nothing looks wrong in isolation. The defect only appears when the question shifts from "does this call work" to "can the person on the other side of this loan move what it returns, and how much would that cost them." That's an adversarial economic question, not a line-reading question, and it's precisely the question a time-boxed manual review is least equipped to answer exhaustively across every asset and market a protocol supports.
Scope compounds it. A lending protocol integrates external tokens, wrappers, and rate sources. An audit bounded to the protocol's own contracts treats the wrapped xStocks rate as an external input and moves on, while an audit of the wrapper would correctly find the wrapper sound. The exploitable condition lives at the junction: a correct wrapper rate, correctly read, used for a purpose it was never safe for. Reviewing either side alone leaves that junction untested.
There's also a timing problem. A protocol that adds new collateral types after launch extends the surface every time. A market added months after the audit inherits a clean report it was never covered by.
How Olympix Would Have Prevented It
Manipulable price sourcing is one of the most well-established detectable vulnerability classes in DeFi, and it's one Olympix targets directly: a raw manipulable spot price used without a time-weighted average or manipulation guard is exactly the pattern the analysis is built to surface.
Applied here, the analysis doesn't need to guess at intent. It follows the value used for collateral pricing back to its source and tests whether that source is manipulable within a single transaction. A rate read live from wrapper state, with no TWAP and no manipulation resistance, fails that test on inspection. BugPoCer takes it further by demonstrating the consequence rather than describing it, flash-loaning capital, inflating the rate, and executing the undercollateralized borrow, producing a proof-of-concept that shows the bad debt appearing before the contract is ever deployed.
The proof-of-concept matters most for this class. A finding that says a price source lacks a TWAP is easy to rank low, because it reads as a hardening suggestion rather than a live vulnerability, especially when the market is small or the asset seems illiquid enough to be safe. A working exploit that borrows against 78x inflated collateral and leaves the protocol insolvent removes the judgment call entirely. The team doesn't have to estimate whether manipulation is economically feasible, because the transaction that does it is sitting in front of them.
This isn't an argument against audits. A skilled human review remains valuable, and a good reviewer will ask where a price comes from. It's an argument that an audit alone isn't a security model, because manipulability is an adversarial property that has to be tested rather than read, and it has to be retested every time a protocol lists a new asset. Continuous, code-level analysis with automated proof-of-concept generation is what tests that property before a market goes live.
Takeaway
Every guarantee a lending market makes depends on the price it uses, so a price an attacker can move isn't a pricing problem, it's a solvency problem. Edel valued wGOOGLx from a live wrapped exchange rate with no time-weighting and no manipulation resistance, and $403K of bad debt followed from a single transaction that made the collateral look 78 times more valuable than it was. The flash loan supplied the size, but the vulnerability was the trusted spot read, and that read was plain Solidity that analysis can follow to its source and prove exploitable before a market ever opens. Testing what a contract is allowed to trust, and proving what happens when that trust is misplaced, is the difference between a lending market that holds and one that ends up holding the loss. To see Olympix trace your price sources and prove the manipulation path against your own contracts, with a working proof of concept for every finding, book a technical walkthrough.
On-Chain References
Chain:            Ethereum mainnet
Protocol:         Edel Finance (Edel Lending, wGOOGLx market)
Attacker:         0x58428161bB55c14A413945f06cbDeC157F411C76
Exploit Tx:       0xe2320086b2815d21b0927839bd0e306466c29a68d38d5361e99dd21ec5472612
Block:            25434062
Flash loan:       180,000 USDC from Morpho
Collateral:       wGOOGLx, priced off the wGOOGLx/GOOGLx wrapped xStocks exchange rate
Loss:             ~$403K protocol bad debt; attacker consolidated to 224 ETH
Vulnerability class: manipulable spot price used for collateral valuation, no TWAP or manipulation guard
Manipulable price sourcing is a class Olympix detects and proves.
More post-mortems
See every post-mortem →

See what Olympix finds on your own code
Send us a repo that's already been audited, and we'll run Olympix at the same commit and show you what comes back.