Find What AI
Can't, and Prove It
Continuous pre-audit security on a formal methods and AI engine. It runs inside your engineering workflow on every change, finds what audits and general AI miss, and proves it.
Audited does not mean secure.
Most exploited contracts had already passed an audit. The problem isn't skipped reviews, it's scope.
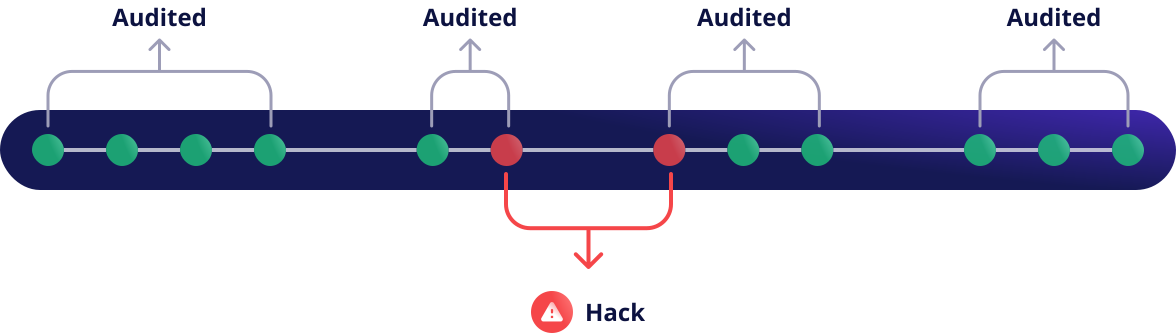
Audits are batched to the delta, a new feature or an updated product, and each scope is validated in isolation, never re-examined in context. The exploit emerges at the boundary: where an audited scope meets the broader system, or where two independently audited scopes interact. Every piece was reviewed. Nothing reviewed how they fit together.
90%
of exploited smart contracts had already been audited.
$22B+
lost to smart contract exploits across the ecosystem to date.
$121M
drained from Balancer in a single 2025 exploit, despite three audits and on-chain monitoring.
Every piece was audited. The seam between them wasn't.
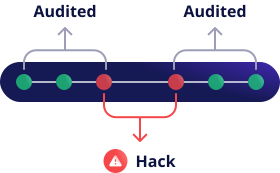
$121M drained
from the Balancer exploit in 2025, at the interaction, not inside a scope.
A probability is a task. A verdict is an answer.
The state space looks infinite. It isn’t.
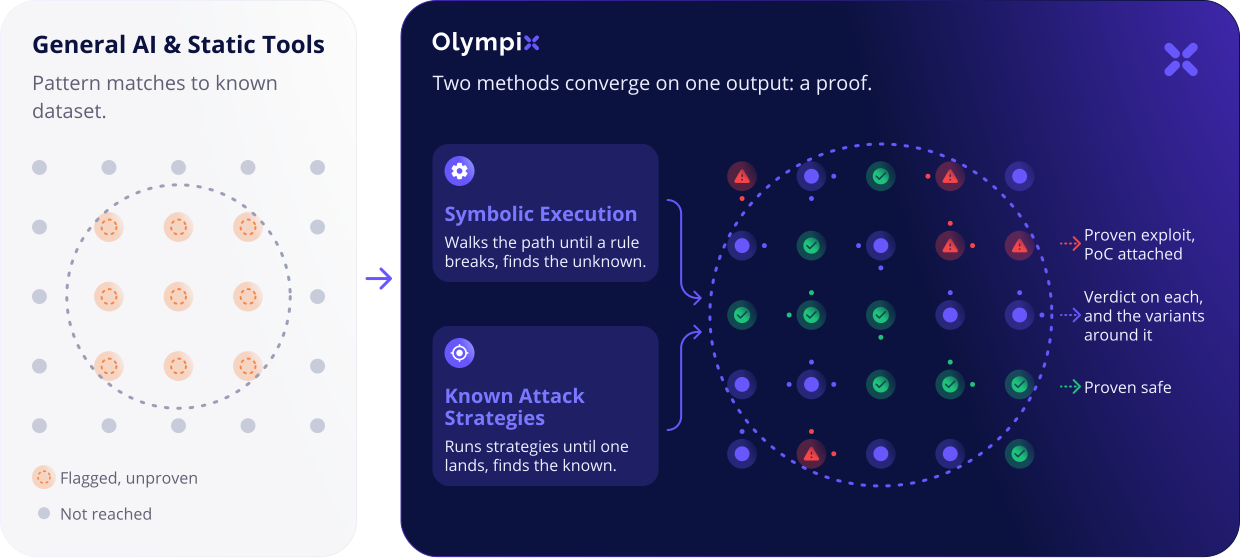
Detection and coverage.
You need both.
Find what is wrong
Catch the known and the unknown
A contract's state space looks infinite. It isn't. Olympix infers the invariants that must hold, maps every path through the code, and attacks each dangerous path two ways at once: symbolic execution until an invariant breaks, and known attack strategies until one lands. Two independent methods, surfacing the known and the unknown, and proving each one exploitable rather than flagging it as a maybe.
Prove nothing is missed
Measured against real attack paths
Detection without coverage is false confidence. Finding issues means nothing if whole regions of the code were never exercised in the first place. The coverage engine measures how much of the system was actually reached, proves the code is genuinely tested against real attack paths, and closes the blind spots that detection alone leaves behind. You get proof of what was checked, not just a list of what was found.
Enforced at every stage, before release.
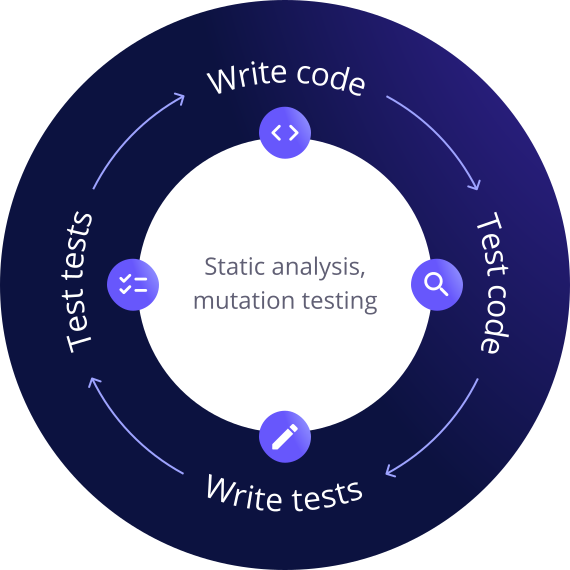
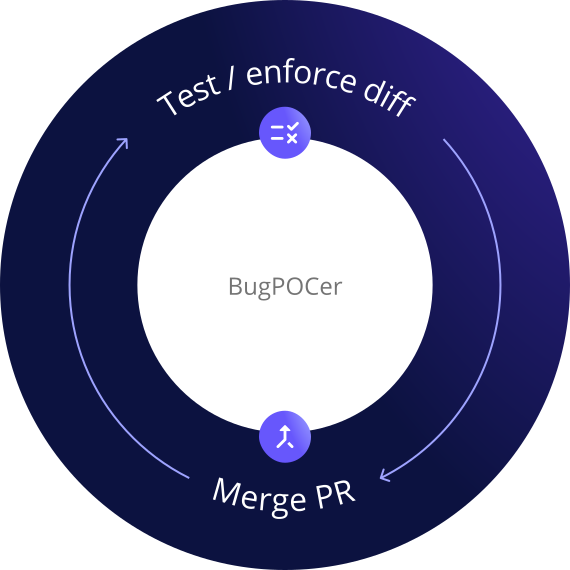
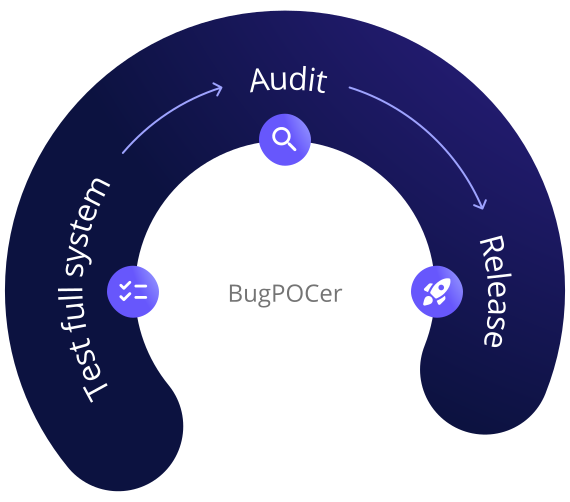
Ongoing development
PR Merges
Gate, blocks merge:
High or medium severity findings, or mutation score below threshold.
Pre-release
Gate, blocks release:
High or medium severity findings.
What it changes in practice
70%
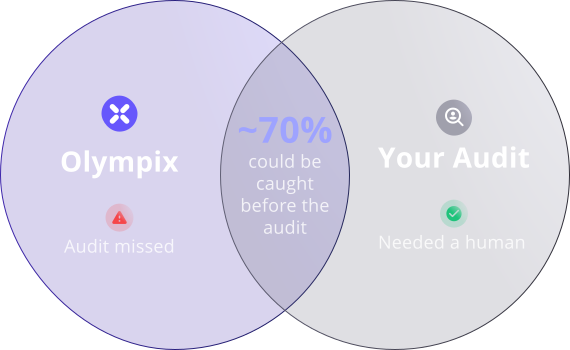
overlap with a typical external audit, cleared before an engagement begins.
$240M
in 2025 code-level losses preventable by Olympix, backtested against real incidents.
$155B
protected on-chain across customers like Uniswap, Circle, and Securitize.
We now go into audits, and ultimately ship to mainnet, with far greater confidence, knowing our code has been through multiple layers of review. Olympix has caught edge-case vulnerabilities early, reduced our mean-time-to-remediate, and reinforced the importance of manual audits as a permanent fixture in our development pipeline.
Deniz Dalkilic
Chief Blockchain Architect | Lumia
With Olympix, security becomes part of our development cycle. Their automation and test generation streamline internal audits, giving our engineers faster feedback and fewer surprises.
Grimmace
Tech Lead | Magpie XYZ
Ask us to prove it.