

Poloniex’s $123M key compromise wasn’t the only failure. Unibot and Maestro both shipped router contracts missing basic input validation — invites for attackers. Astrid let fake tokens slip through faulty withdrawal logic. In each case, either the access was too open or the checks were too weak. The result: $124M gone, all preventable.
On November 10th, the Poloinex exploit on multiple chains resulted in a $123M loss due to the compromise of private keys. The attacker drained $57 million worth of ETH, $47 million worth of TRON, and $19 million worth of BTC. Poloinex confirmed the exploit and stated that a portion of the stolen assets has been frozen, ensuring affected customers would be reimbursed. Additionally, a 5% bounty was offered to the hackers. In response to the incident, Poloinex temporarily suspended deposits and withdrawals, which resumed on November 15th.
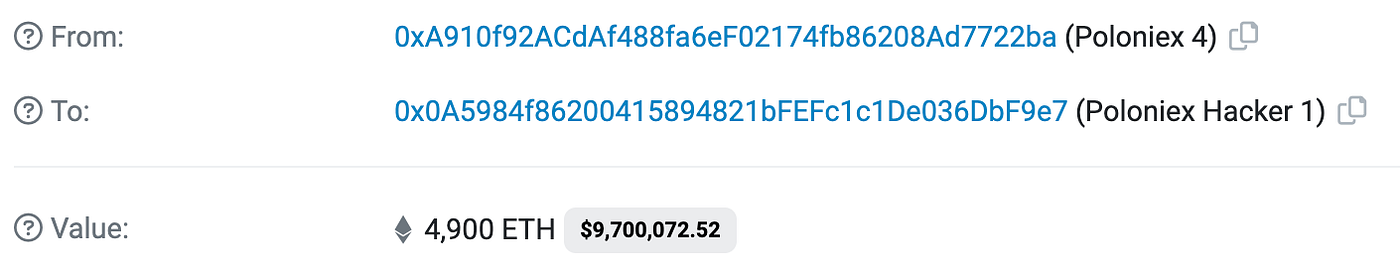
Exploit Contract: 0xA910f92ACdAf488fa6eF02174fb86208Ad7722ba
Transaction Hash: 0xcbf1547119ae869604585997b11d118bb423f32ae75c2fe055b7eb8d79d3ae77
On October 31st, the Unibot exploit on the Ethereum Mainnet resulted in a $640K loss. The root cause of the hack was the lack of input validation in Unibot’s router contract, which had been deployed on October 28th. The attacker called the 0xb2bd16ab() function with an arbitrary address, triggering the transferFrom() function and enabling the unauthorized draining of funds. The Unibot router contract remains unverified on the Ethereum blockchain.

Exploit Contract: 0x126c9FbaB3A2FCA24eDfd17322E71a5e36E91865
Transaction Hash: 0xcbe521aea28911fe9983030748028e12541e347b8b6b974d026fa5065c22f0cf
On October 28th, the Astrid Finance exploit on the Ethereum Mainnet resulted in a $228K loss due to logic vulnerability. The exploit’s root cause was the attacker’s ability to mint and deploy fake tokens through the call to the withdraw() function in the AstridProtocol contract. This action enabled the attacker to claim allowance and generate a profit. The Astrid Finance team acknowledged the exploit, refunded the affected users, and provided a 20% bounty to the hackers.
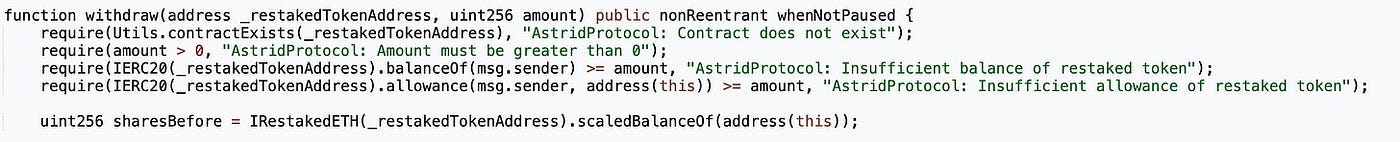
Exploit Contract: 0x4d5b4b9ccf52bbcfe7b71b3038d8577293779e0c
Transaction Hash: 0x8af9b5fb3e2e3df8659ffb2e0f0c1f4c90d5a80f4f6fccef143b823ce673fb60
On October 24th, the Maestro exploit on the Ethereum Mainnet resulted in a $502K loss. The root cause of the hack is similar to the root cause of the Unibot incident, where the router contract lacked input validation. The attacker called the 0x9239127f() function with an arbitrary address, triggering the transferFrom() function and enabling the unauthorized draining of funds. Maestro confirmed the exploit and suspended the functionalities of their router contract.

Exploit Contract: 0x8eae9827b45bcc6570c4e82b9e4fe76692b2ff7a
Transaction Hash: 0xc087fbd68b9349b71838982e789e204454bfd00eebf9c8e101574376eb990d92