
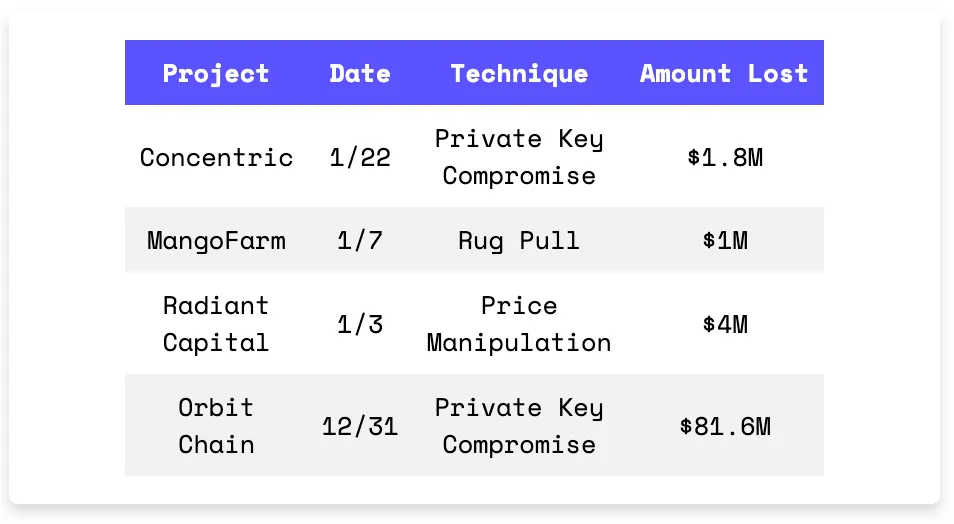
Orbit Chain lost $81.6M after its owner key signed off on withdrawals. Concentric’s deployer key let the attacker mint and drain. Radiant Capital got front-run six seconds post-deploy into a $4M price manipulation. MangoFarm faked its way to a $1M exit. From stolen keys to uninitialized markets, these aren’t isolated incidents; they’re systemic lapses in deploy-time security.
On January 22nd, the Concentric exploit on the Arbitrum chain resulted in a $1.8M loss. The root cause of the exploit was a compromise of the deployer key, which allowed the attacker to update the CONE-1 contract. Following the update, the attacker was able to call the public adminMint() function and drain funds from the liquidity pool. The Concentric team acknowledged the incident and suspended all transactions.
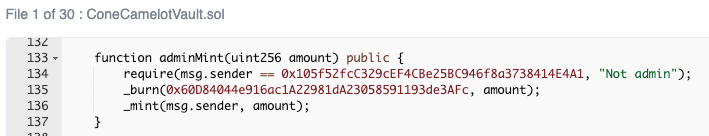
Exploit Contract (on Arbitrum Chain): 0xf36c407f3c467e9364ac1b2486aa199751ba177d
Transaction Hash: 0x00554de194cb38fc13df9de672e7551ec876b921b73c81da185d7231c8e43bcd
On January 7th, the MangoFarm rug pull on the Ethereum mainnet resulted in a $1M loss. The exploiters impersonated Mango Markets, which is another decentralized finance platform, to deceive users. Both the MangoFarm Twitter account and website are now inaccessible.
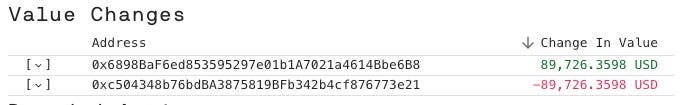
Exploit Contract: 0xc504348b76bdba3875819bfb342b4cf876773e21
Transaction Hash: 0xc5c6a4fccb263a7e702f2ef35336916ff0ca221524735beccca7001381e6be17
On January 3rd, the Radiant Capital exploit on the Arbitrum chain resulted in a $4M loss The root cause of the attack was a price manipulation vulnerability in newly deployed contracts lacking liquidity. The attacker identified Radiant Capital’s most recent contract and deposited funds into it just six seconds after deployment. This action enabled the attacker to manipulate the price of the rUSDCn token and make a profit. The Radiant Capital team confirmed that they are working on recovering the stolen assets.
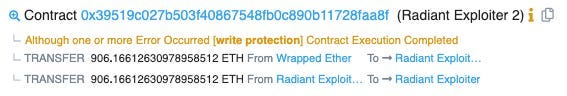
Exploit Contract (on Arbitrum Chain): 0xc0249d743a17ed44b4f9ee611b51d26ab2e26444
Transaction Hash: 0xc5c4bbddec70edb58efba60c1f27bce6515a45ffcab4236026a5eeb3e877fc6d
On December 31st, the Orbit Chain exploit on the Ethereum mainnet resulted in a $81.6M loss. The root cause of the exploit was a compromise of the owner’s private key. The attacker was able to create signatures for the private _validate() function using the private key. The drained funds include ETH, USDT, USDC, DAI, and WBTC tokens. The total value locked (TVL) on Orbit Chain has decreased from $152M to $61.8M.
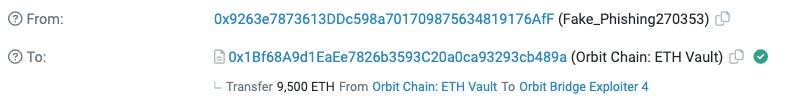
Exploit Contract: 0x1bf68a9d1eaee7826b3593c20a0ca93293cb489a
Transaction Hash: 0x639d27e564214411ad8eb06cf00d85cd90f83503a53ab5bf35dd5c6e1148ae0a