
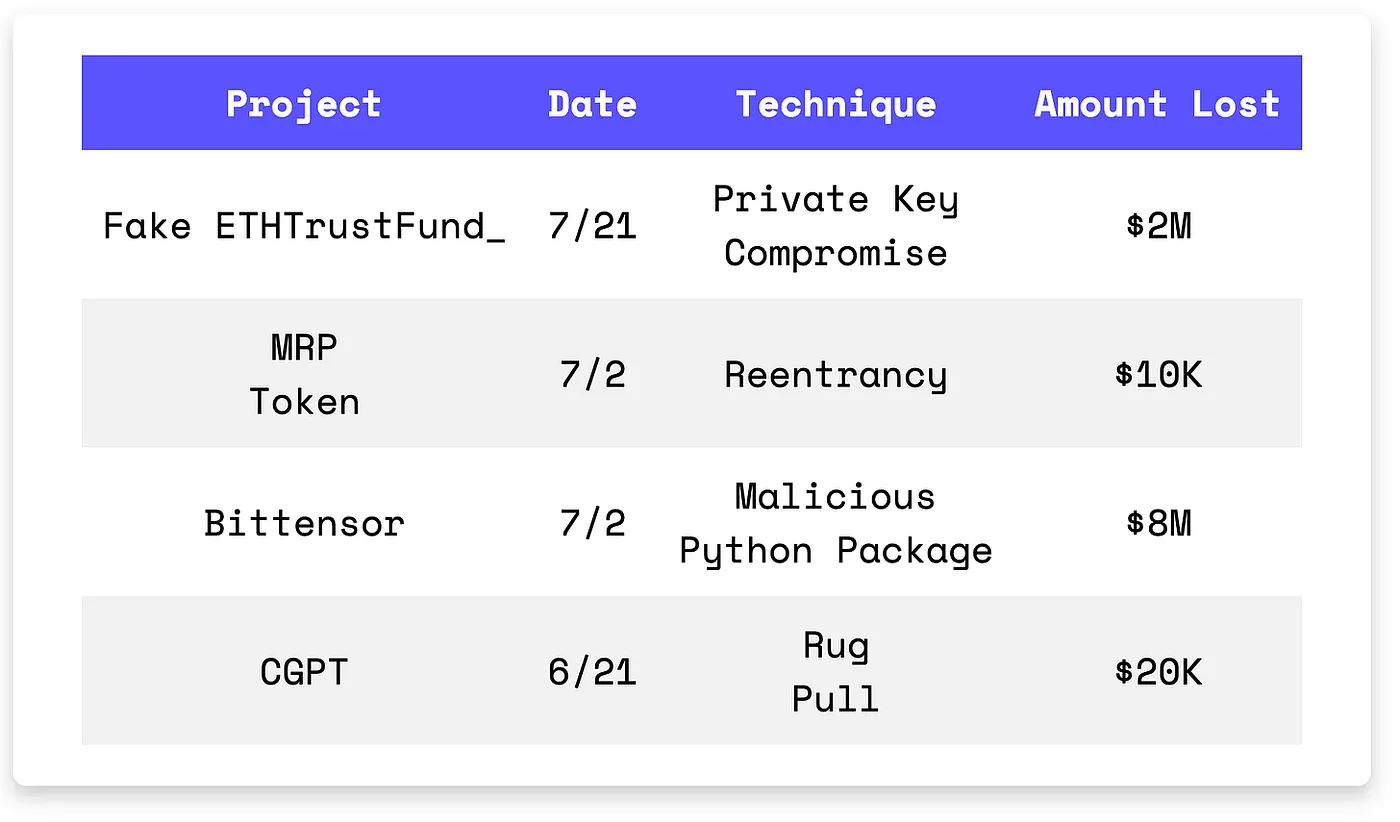
A rogue Python release drained $8M from Bittensor wallets. Fake ETHTrustFund_ lost $2M to a treasury key compromise. CGPT impersonators rugged users for $20K. A subtle WMRP reentrancy bug cost $10K. Social engineering and unchecked dependencies remain critical attack vectors.
On July 21st, the Fake ETHTrustFund_ exploit on the Base Chain resulted in a $2M loss. The root cause was the compromise of Fake ETHTrustFund_’s treasury wallet. The exploiter drained 3.2M BRETT coins and 477 ETH in two separate transactions. The stolen assets were later funneled into Tornado Cash and Railgun.

Exploit Contract (on Base): 0x532f27101965dd16442e59d40670faf5ebb142e4
Transaction Hash: 0x2a7af282f777253ae4aa43679ba79658a77c45502040ea14fcae4bb183f88091
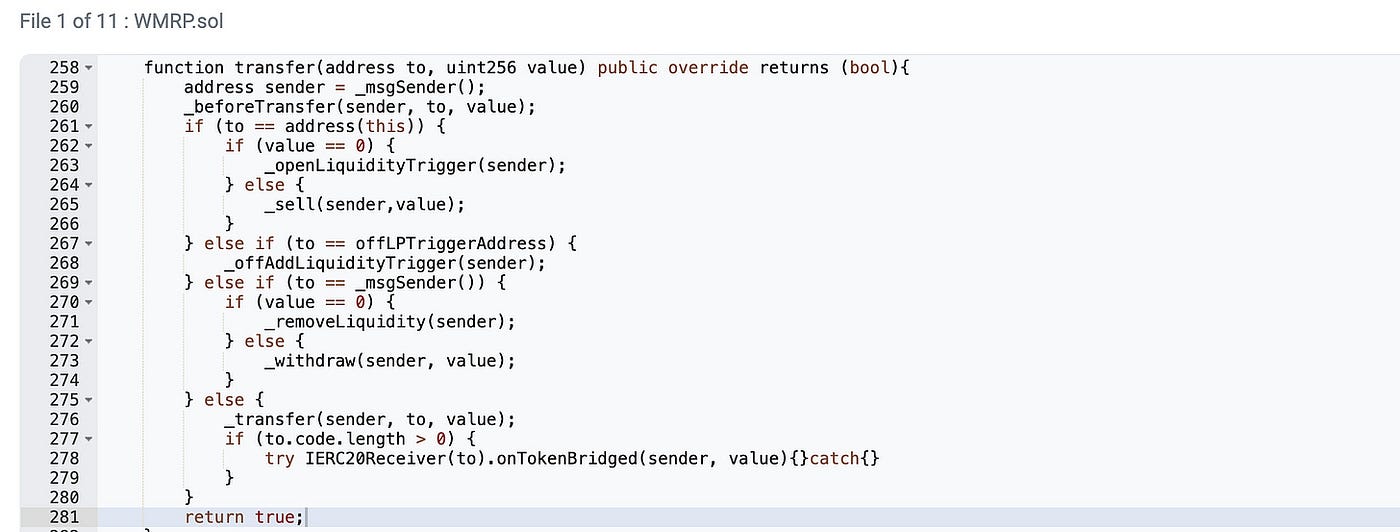
On July 2nd, the MRP token expoit on the BNB chain resulted in a $10K loss. The root cause was a reentrancy vulnerability in the WMRP wrapped-token contract’s transfer() function. The attacker transferred WMRP tokens to themselves with a value of 0, triggering the fallback function during liquidity removal. This manipulation allowed the attacker to re-enter the receive function and transfer BNB to the WMRP contract.
Exploit Contract (on BNB Chain): 0x35F5cEf517317694DF8c50C894080caA8c92AF7D
Transaction Hash: 0x4353a6d37e95a0844f511f0ea9300ef3081130b24f0cf7a4bd1cae26ec393101
On July 2nd, the Bittensor exploit resulted in a $8M loss. The root cause was a malicious Python package in version 6.12.2 of Bittensor, which contained code to steal unencrypted coldkey details. When users downloaded this package and decrypted their coldkeys, the information was sent to a remote server controlled by the attacker, leading to the unauthorized transfer of 32,000 TAO tokens. The Bittensor team swiftly responded by putting the chain into “safe mode,” halting all transactions.

Exploit Contract (on Bittensor Network): 5HHWXozwYUqYHZSrfDCaZSdhNrvDgkPha48zCgvEddeqR66x
Transaction Hash: 0x321bd115b2485b14656b83adbfd9ef575ea5a2b663b260e4d1da046307c944a5
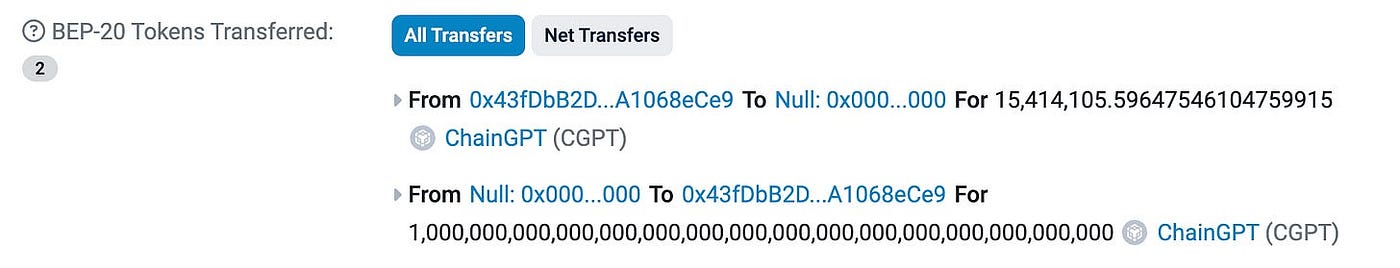
On June 21st, the CGPT rug pull on the BNB chain resulted in a $20K loss. The exploiters impersonated ChainGPT, which is another decentralized platform, to deceive users. Both the CGPT Twitter account and website are now inaccessible.
Exploit Contract (on BNB Chain): 0xc6f688cf2694298667830de83c020b16eeae5a45
Transaction Hash: 0x70de56f67d330a1749c5527f1427b1efb766f3fc5f005a4234ec546b786b2d1d