
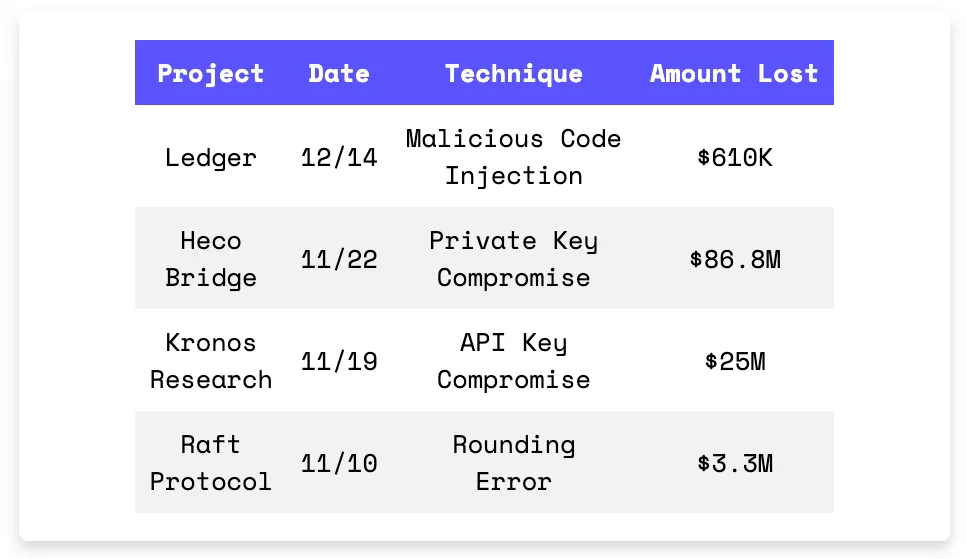
Ledger’s $610K exploit wasn’t on-chain — it was in the supply chain, via a poisoned NPM package. Heco Bridge lost $86.8M to key compromise, while Kronos Research lost $25M to leaked API credentials. Raft Protocol? $3.3M gone due to precision flaws in share minting logic. These weren’t contract bugs; they were infrastructure failures — up and down the stack.
On December 14th, the Ledger exploit on multiple chains resulted in a $610K loss. The root cause of the exploit was that a former Ledger employee had their NPM JS account compromised. Since Ledger relied on a CDN without a version constraint, the attacker was able to inject malicious code into the @ledgerhq/connect-kit npm library. This malicious code allowed the attacker to drain funds and make a profit. Multiple DeFi platforms including PancakeSwap, SushiSwap, and Harvest Finance were affected.
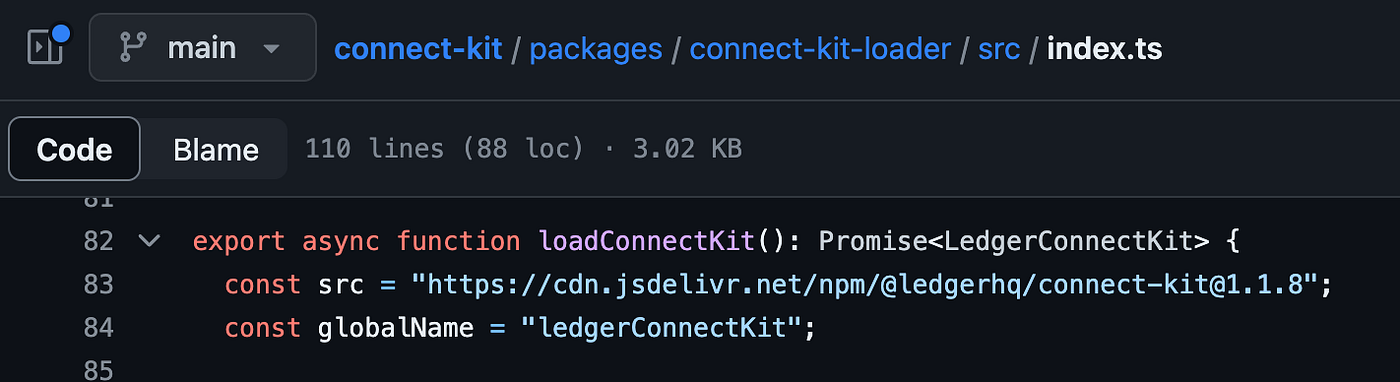
Exploit NPM Library: https://github.com/LedgerHQ/connect-kit/blob/main/packages/connect-kit-loader/
On November 22nd, the Heco Bridge exploit on the Ethereum Mainnet resulted in a $86.8M loss due to the compromise of private keys. The attacker was able to withdraw funds, exploiting vulnerabilities in the withdrawal() function. The initial targeted hot wallet was drained for 4.25M KOK tokens and 2.19M ARIX tokens. Other stolen assets include USDT, HBTC, SHIB, UNI, USDC, LINK, ETH, and TUSD. The HTX team acknowledged the incident and assured the affected users would be compensated
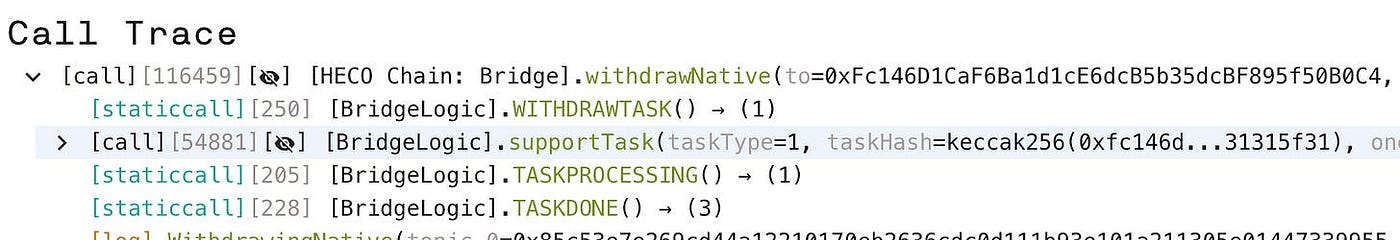
Exploit Contract: 0x6b2980979d29c15c6438fff1cb9c1e4127370969
Transaction Hash: 0xbb6fe88427c2f3bc179075109d47a805dcfedab0e475eaca0d979311873e131b
On November 19th, Kronos Research exploit on the Ethereum Mainnet resulted in a $25M loss. Kronos Research announced the root cause as the unauthorized access of their API keys. The attacker executed six transactions, transferring varying amounts of ETH to different addresses. The Kronos team acknowledged the exploit, halted all trading, and stated that losses totaling over 12,800 ETH are not a substantial portion of its equity.
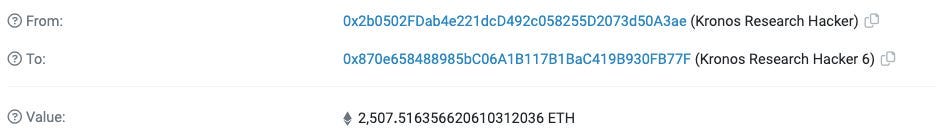
Exploit Contract: 0x2b0502FDab4e221dcD492c058255D2073d50A3ae
Transaction Hash: 0x3a24b938eb3c446b3dfcb42fb1430ac65020df95a9c9595986ed6cfb37739cb3
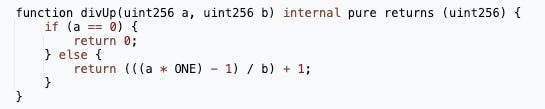
On November 10th, the Raft Protocol exploit on the Ethereum Mainnet resulted in a $3.3M loss due to a precision calculation flaw during share token minting. The attacker borrowed 6,000 cbETH in flash loans from AAVE, and transferred 6,001 cbETH to the InterestRatePositionManager contract, subsequently liquidating a pre-existing position. Exploiting a precision flaw, the attacker amplified the cbETH balance, minting 1 wei share through the divUp() function’s manipulation. By manipulating index values, the attacker minted an inflated amount of R tokens. The attacker then sold 6.7M R tokens for 1,575 ETH across various pools and made a profit.
Exploit Contract: 0x9ab6b21cdf116f611110b048987e58894786c244
Transaction Hash: 0xfeedbf51b4e2338e38171f6e19501327294ab1907ab44cfd2d7e7336c975ace7