
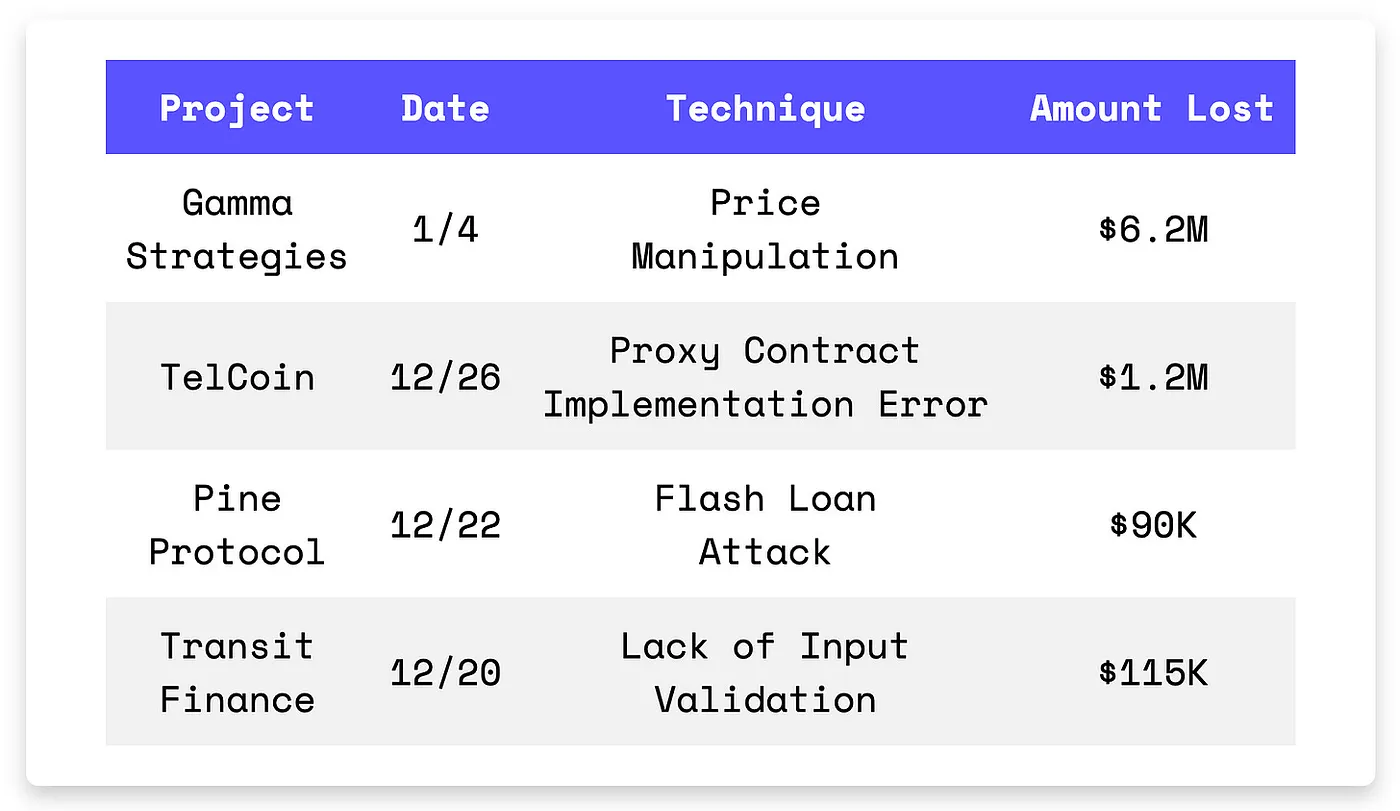
Gamma Strategies’ $6.2M loss came down to a 200% price change threshold that ignored flash loan realities. TelCoin’s proxy setup reused slot 0, letting attackers reinitialize logic contracts for $1.2M. Pine Protocol’s upgrade path introduced cross-version lending holes, and Transit Finance skipped token validation in a swap router. These aren’t novel vectors, they’re recurring footguns wrapped in different wrappers.
On January 4th, the Gamma Protocol exploit on the Arbitrum chain resulted in a $6.2M loss. The attacker used flash loans and deposited the funds into Gamma Strategies’ Hypervisor contract, artificially inflating the USDC.e token’s price and enabling the attacker to gain profits. Gamma Strategies acknowledged the incident, stating that the price change threshold to prevent flash loan attacks was set too high, allowing a price change range of up to 200%. They assured that the price change threshold would be lowered to avert future exploits.
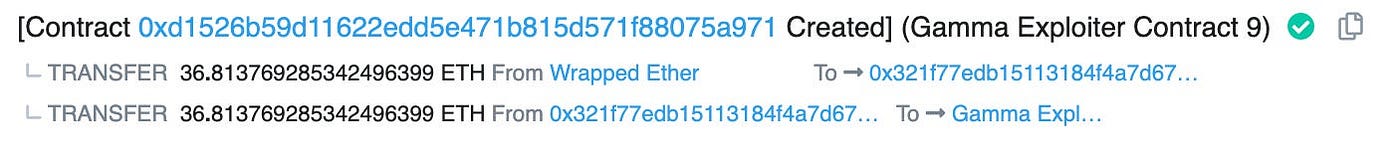
Exploit Contract (on Arbitrum chain): 0x45EF94207E84d667D739270eE0e65AD311f74B34
Transaction Hash: 0x1b9911770ef30e51ecec6992c623c79af9871e2898d34f2adaeb8a8ab1a75354
On December 25th, the TelCoin exploit on the Polygon chain resulted in a $1.2M loss. The exploit’s root cause was an initialization error during the proxy contract deployment. The attacker took advantage of a mismatch in storage slot 0 between the proxy and implementation contracts, allowing reinitialization of malicious contracts. There were a total of 4,958 transactions to drain funds. TelCoin acknowledged the incident and restored balances for all affected users.
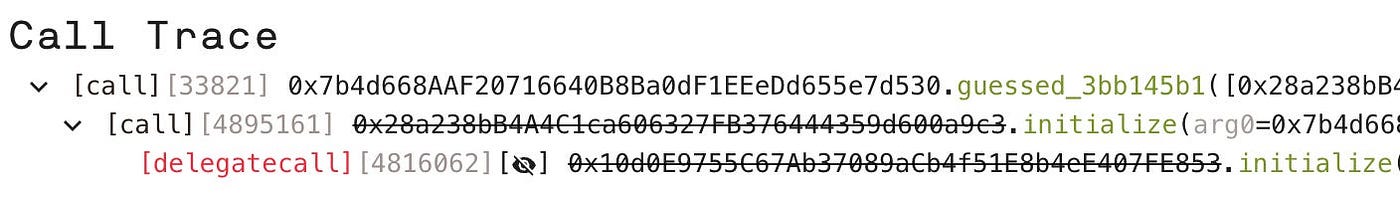
Exploit Contract (on Polygon chain): 0xdf7837de1f2fa4631d716cf2502f8b230f1dcc32
Transaction Hash: 0x8f5bd1eb63ec45026617940cd37e4e3b1f4848ecaf66f57a126c9f24b089ca9b
On December 22nd, the Pine Protocol exploit on the Ethereum Mainnet resulted in a $90K loss. The root cause of the exploit was that Pine Protocol’s shared pools between old and new contract versions enabled an attacker to exploit fund transfers from a single address to different pools. The attacker used this flaw to borrow assets from the new version contract, using them as collateral to borrow more from the old version contract. After repaying the debt to the new version contract, both old and new version contracts wrongly assumed all debt was paid.
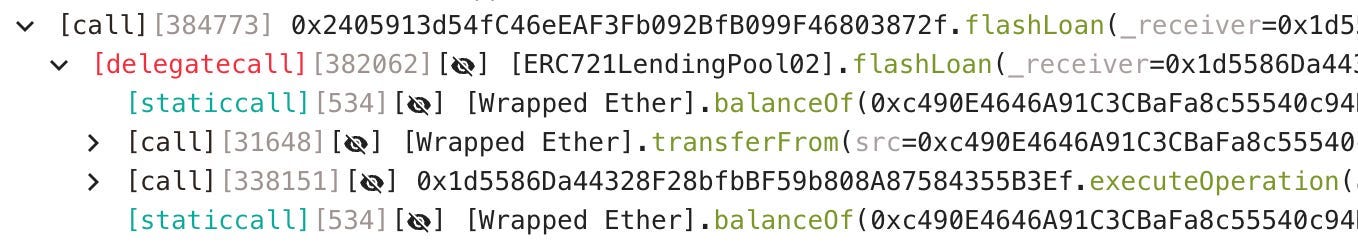
Exploit Contract: 0x2405913d54fc46eeaf3fb092bfb099f46803872f
Transaction Hash: 0x88db033171344c7b89d50f48e1e50ef3a622371cf3ab997613469904838c83ad
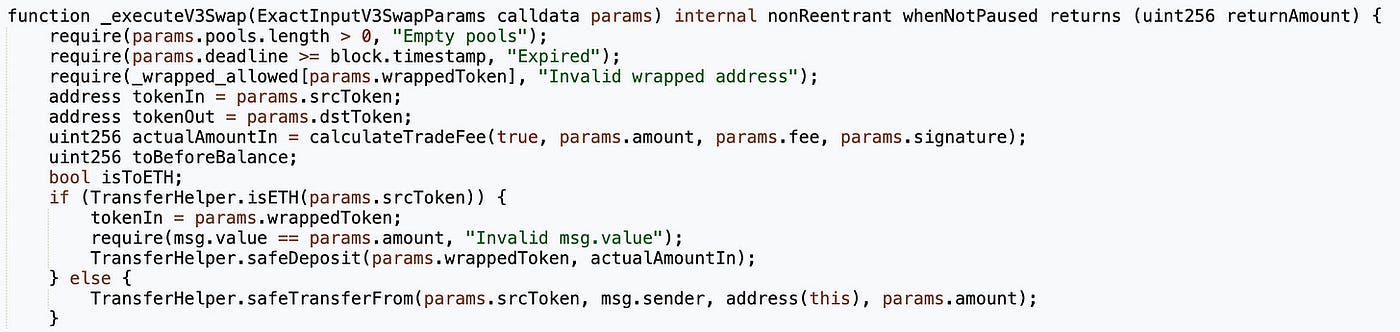
On December 20th, the Transit Finance exploit on the BNB chain resulted in a $115K loss. The root cause of the hack was the lack of input validation in Transit Finance’s UniswapV3Router contract. The attacker called the private _executeV3Swap() function with a fake token pair and was able to manipulate the actualAmountIn value. This vulnerability allowed the attacker to drain a total of 36 ETH and 147 BNB.
Exploit Contract (on BNB chain): 0x00000047bb99ea4d791bb749d970de71ee0b1a34
Transaction Hash: 0x93ae5f0a121d5e1aadae052c36bc5ecf2d406d35222f4c6a5d63fef1d6de1081