
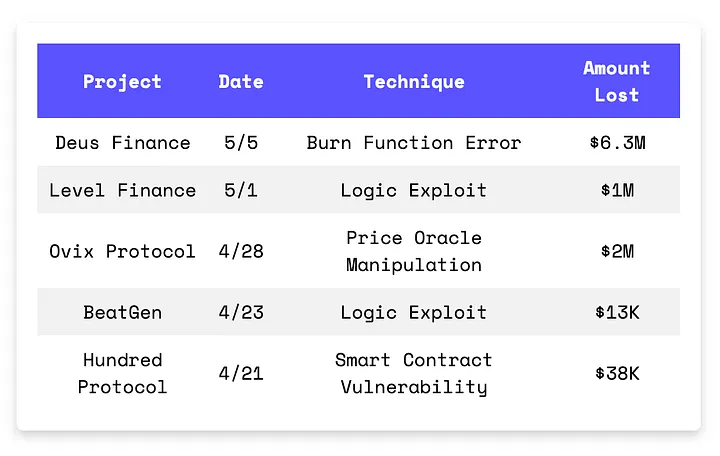
Five different bugs, one shared failure mode: trusting your own code too much. Deus let token allowances invert due to a miswired mapping. Ovix trusted a single oracle. Level forgot to accumulate rewards. Unlock skipped caller checks entirely. These weren’t novel attacks; they were the inevitable result of treating implementation as truth. Together, they cost over $9M.
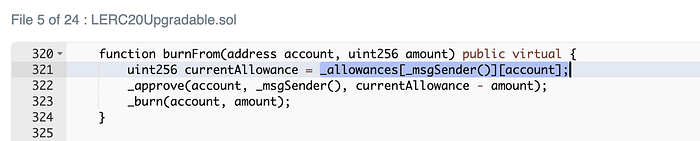
Deus Finance’s token contract was exploited due to an implementation error. The attacker targeted addresses holding large amounts of $DEI tokens and gained approval to transfer coins from the victim’s address to the attacker’s address. The implementation flaw was caused by incorrect mapping of allowances, which should have been mapped as _allowances[address _owner][address _spender], instead of _allowances[address _spender][address _owner]. This allowed the attacker to approve the burning and transferring of the victim’s tokens. The exploit resulted in a loss of over $5M on Arbitrum and $1.3M on BNB Chain. Deus confirmed that they paused all contracts on all chains and that the exploiter returned 2023 ETH worth almost $4M.
Transaction Hash (on Arbitrum): 0xb1141785b7b94eb37c39c37f0272744c6e79ca1517529fec3f4af59d4c3c37ef
Attacker: 0x189cF534de3097C08B6bEAF6EB2B9179DAb122d1
Exploit Contract: 0xBC1b62dB243B51dabCd9540473324f36E094EC55
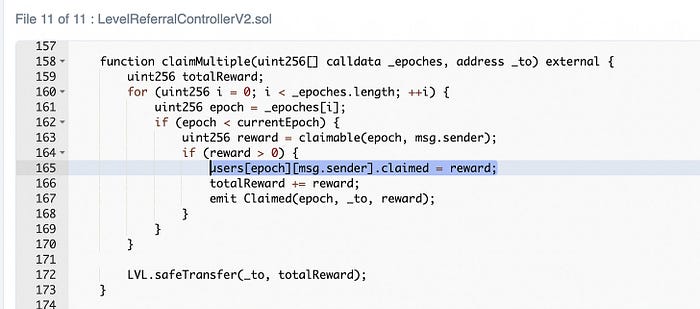
An attack on Level Finance on BNB Chain resulted in a loss of $1M. The hacker exploited a vulnerability in Level Finance’s LevelReferralControllerV2 smart contract. The claimMultiple function in this contract calculated the claimed reward incorrectly by resetting it for each epoch rather than accumulating (users[epoch][msg.sender].claimed = reward instead of += reward). This allowed the hacker to submit the same epoch to claim the reward multiple times.
Transaction Hash (on BNB Chain): 0x6ecc8c6cc80446a3f4a8aee7a1c93337f653d8658b3720c74ed09bf38e26c966
Exploit Contract: 0x9F00fbD6c095D2C542687Ed5afB68D9c3fB2F464
The Ovix Protocol on Polygon suffered a hack on April 28, allowing an attacker to manipulate the price oracle. The attacker flash loaned 5.4M USDT + 720K USDC, and used the fund to borrow vGHST tokens, which altered the price oracle as it was reliant on the conversion rate between vGHST and GHST. The attacker then returned the borrowed vGHST, but at a modified exchange rate, allowing them to sell the tokens at a higher price and make a $2M profit. To prevent similar attacks, it is recommended to use multiple price oracles for the same asset to compare the results and identify any discrepancies that may indicate manipulation, known as oracle aggregation.

Transaction Hash (on Polygon): 0x10f2c28f5d6cd8d7b56210b4d5e0cece27e45a30808cd3d3443c05d4275bb008
Attacker: 0x702Ef63881B5241ffB412199547bcd0c6910A970
Exploit Contract: 0x51195e21BDaE8722B29919db56d95Ef51FaecA6C
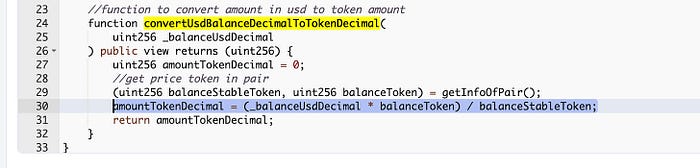
On April 23rd, BeatGen on BNB Chain suffered a $13K hack due to a logic exploit in their Oracle smart contract. The exploit occurred in the convertUsdBalanceDecimalToTokenDecimal function, which calculated the decimal amount of the BeatGen token (BNG) by using the ratio of the BNG token balance to the stable coin balance. Therefore, the BNG decimal amount is inversely proportional to the stable coin balance. The attacker took advantage of this logic by reducing the balance of the stable token to increase the amount of the token decimal and gain profits.
Transaction Hash (on BNB Chain): 0xd0f3c8e703ce81fbe677da0b6d37c397361d7789b090327d2e4ca32916dcb639
Attacker: 0x84fd453f80377ea49a40087290688d01af81fa1b
Exploit Contract: 0xdee162456705da4e8184ca5ea75b0c107fa21a0d
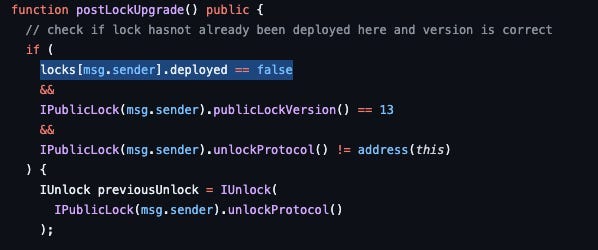
The Unlock Protocol was hacked, resulting in a loss of $38K. The attacker exploited the UnlockV12 contract by taking advantage of a missing caller verification. First, the attacker deposited funds from Tornado into their attack contract. Then, the contract called the postLockUpgrade function and ‘locked’ the contract address by setting the deployed value to true. This allowed the msg.sender to bypass the deployed/locked checks and transfer funds to the attacker’s contract. The drained ETH funds were subsequently deposited into Tornado.
Transaction Hash: 0x4ac413c3c6edd445d1f09cd770d6aafab19b0b58fde7d0cefc74e17265033ef6
Attacker: 0x43ee4169d9ff5e5b10ca42923b1e5d07a157bb71
Exploit Contract: https://github.com/unlock-protocol/unlock/blob/48b435c2683439c1001fe089869943c4911649c7/packages/contracts/src/contracts/Unlock/UnlockV12.sol