

Cork Protocol dropped $12M from an unguarded Uniswap V4 hook. ResupplyFi let 1 wei unlock $9.6M via a vault price trick. Meta Pool’s un-overridden mint logic let attackers mint without deposits. And Force Bridge? Admin keys stolen after shutdown. It’s always the missed check, the dangling override, or the ghost key that costs millions.
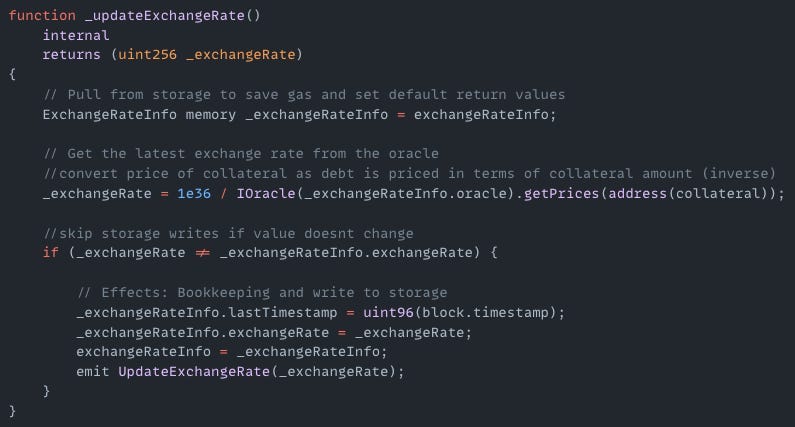
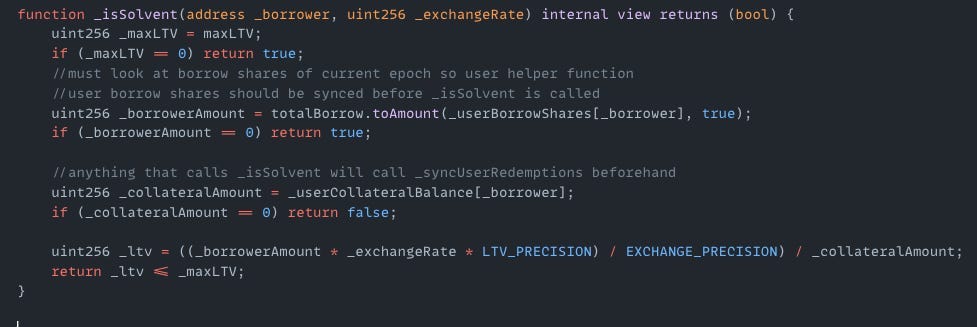
On June 26, the ResupplyFi exploit on the Ethereum mainnet resulted in a $9.6M loss due to a price manipulation attack. The attacker took advantage of a new lending contract with no prior deposits to manipulate the pricePerShare of a vault. The attacker made a large donation to an empty cvcrvUSD vault and artificially inflated the vault’s pricePerShare. The private _updateExchangeRate() function then calculated the exchange rate (1e36 / price) as zero due to the inflated denominator. As a result, the _isSolvent() check calculated LTV = 0. This allowed the attacker to borrow 10M reUSD with 1 wei of collateral.
Exploited Contract: 0x6e90c85a495d54c6d7e1f3400fef1f6e59f86bd6
Transaction: 0xffbbd492e0605a8bb6d490c3cd879e87ff60862b0684160d08fd5711e7a872d3
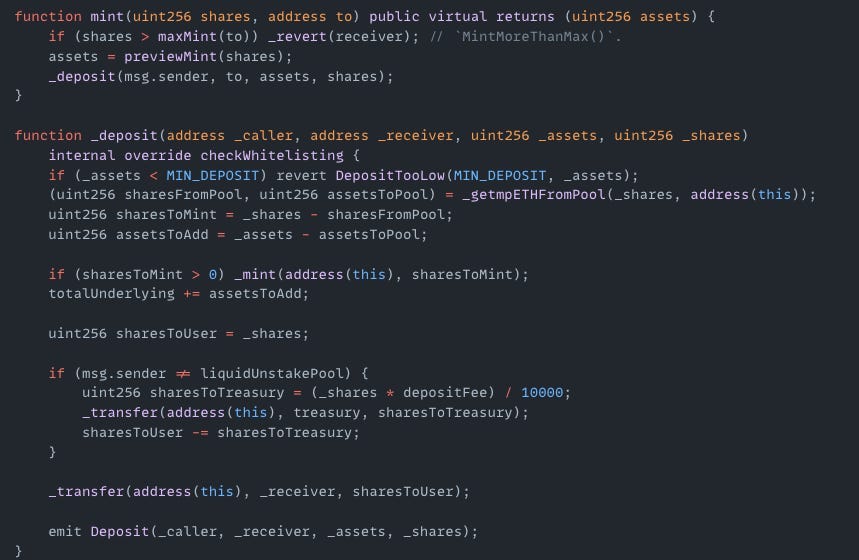
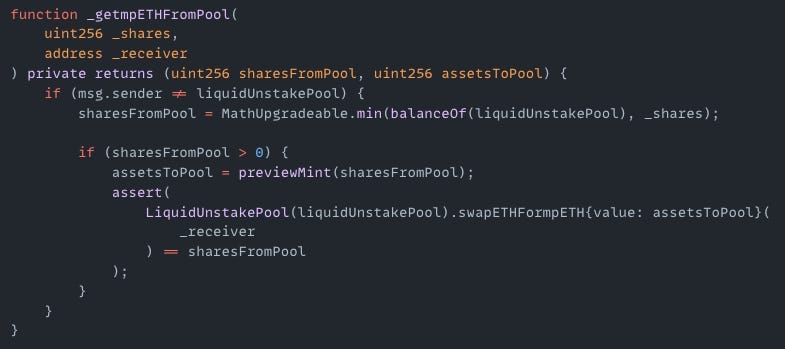
On June 17, the Meta Pool exploit on the Ethereum mainnet resulted in a $137K loss. The root cause of the exploit was a missing override on the mint() function inherited from ERC4626. The attacker first used a flash loan to drain all mpETH from liquidUnstakePool, which allowed to bypass the _getmpETHFromPool() check (refer to the function code below; if the liquidUnstakePool holds zero mpETH, sharesFromPool becomes zero). The attacker was then able to minT mpETH without depositing any ETH.
Exploited Contract: 0x3747484567119592ff6841df399cf679955a111a
Example ERC4626 Contract: https://github.com/Vectorized/solady/blob/main/src/tokens/ERC4626.sol
Transaction: 0x57ee419a001d85085478d04dd2a73daa91175b1d7c11d8a8fb5622c56fd1fa69
On June 1, the Force Bridge exploit on the BNB chain and Ethereum mainnet resulted in a $3.8M loss due to a private key compromise. The attacker got unauthorized access to admin keys the day after Force Bridge announces it ceasing operations. The attacker targeted bridge contracts and stole USDT, USDC, ETH, DAI, WBTC tokens.
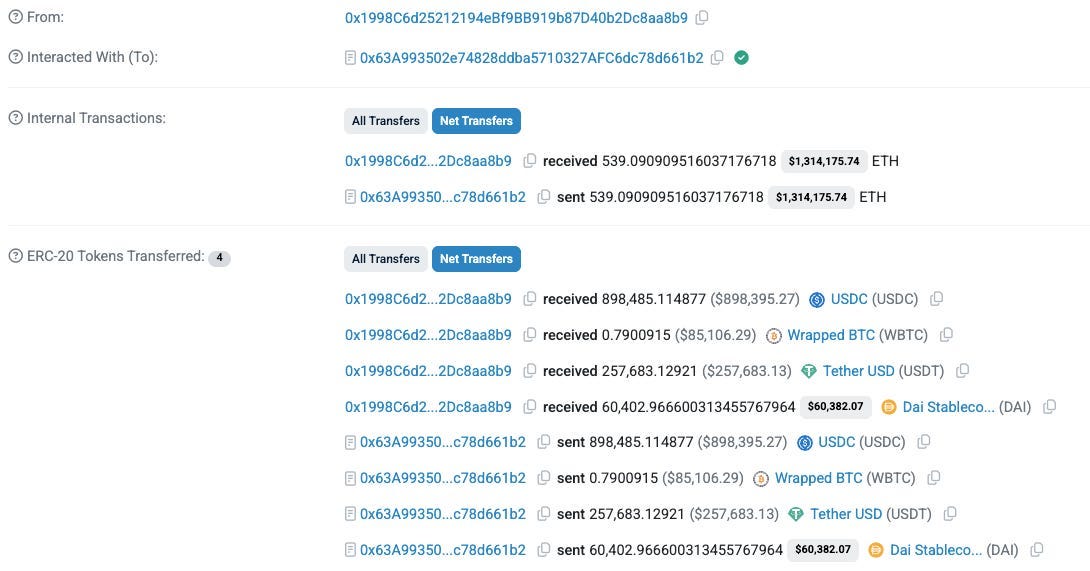
Transaction: 0x6b6fbd9d6beef56d2a4f0d14852beea381764b962d7d73ecd216b9fd991299a1
On May 28, the Cork Protocol exploit on the Ethereum mainnet resulted in a $12M loss. The root cause of the exploit was missing proper authorization checks in Cork Protocol’s Uniswap V4-based hook system. The attacker first bought 2.5 Depeg Swaps 19 minutes before expiry, generating a fake annualized risk premium of 1,779 quadrillion percent. This artificially inflated the historical yield average (HIYA), which the next market cycle used to price new Cover Tokens. As a result, the attacker converted 0.0000029 wstETH into over 3,760 CTs post-rollover. The attacker then called the beforeSwap() function with forged parameters, claiming to be the original caller, to have paid the required redemption asset (RA), to be minting Cover and Depeg tokens from a valid market, and to be using a legitimate market ID. Since this function lacked proper authorization controls, it treated the attacker as a valid buyer and transferred reserved Depeg Swaps to their proxy market.
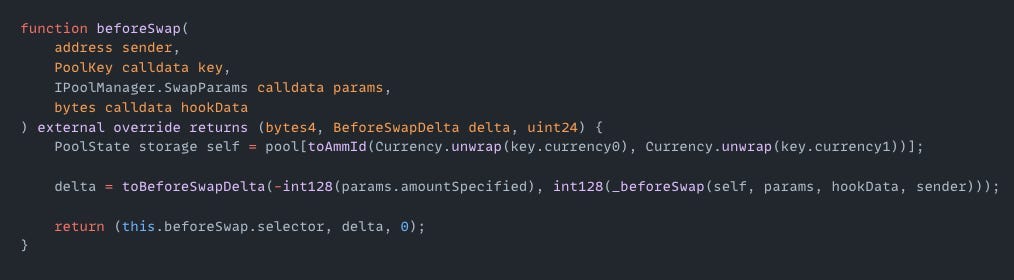
Exploited Contract: 0x5287e8915445aee78e10190559d8dd21e0e9ea88
Step 1 Tx (Risk Premium Increase: 0x14cdf1a643fc94a03140b7581239d1b7603122fbb74a80dd4704dfb336c1dec0
Step 2 Transaction (converting wstETH to Cover Token): 0xfd89cdd0be468a564dd525b222b728386d7c6780cf7b2f90d2b54493be09f64d