
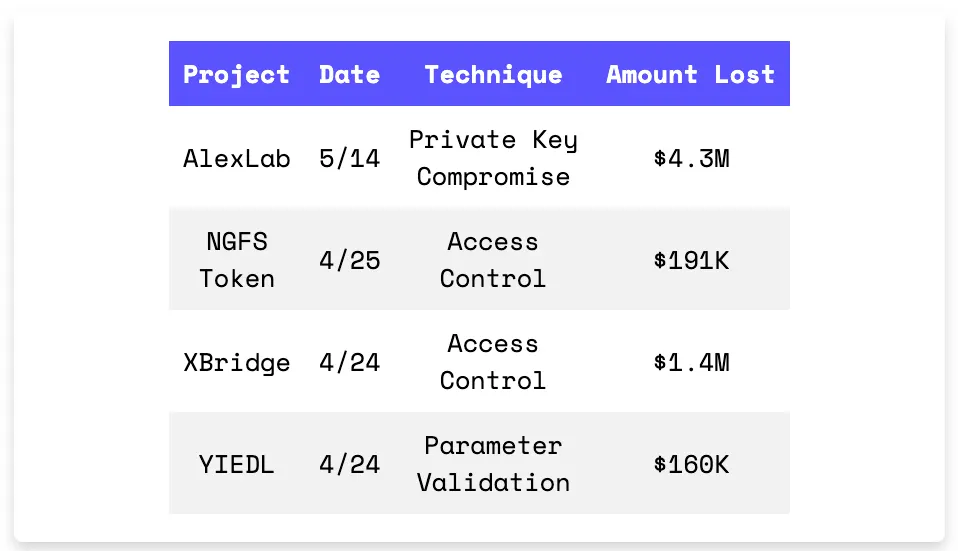
AlexLab lost $4.3M after private key compromise gave control of its bridge. NGFS leaked $191K from an unprotected delegate call. XBridge bled $1.4M via unchecked token listing. YIEDL was drained for $160K due to parameter abuse. Four vectors, same verdict: access control is still broken by default.
On May 14th, the AlexLab exploit on the BNB network resulted in a $4.3M loss. The root cause of the hack was a compromised private key, allowing the attacker to take control of AlexLab’s XLink bridge. The attacker drained 16 BTBC, 3.3M BSC, and 2.8M SKO tokens. AlexLab confirmed the exploit and offered a bounty of 10% of the stolen funds for their return.

Exploit Contract (on BNB Chain): 0xb3955302e58fffdf2da247e999cd9755f652b13b
Transaction Hash: 0x47e123af93add709bc2516f6a5db057dfbb1d66a75b693cd7980cd3eb28c7357
On April 25th, the NGFS Token exploit on the BNB chain resulted in a $191K loss. The root cause was insufficient access control in the NGSFToken contract. The delegateCallReserves function had public visibility and lacked proper restrictions, allowing the attacker to configure the _uniswapV2Proxy variable arbitrarily. The attacker set their contract as a UniSwapV2 proxy via the setProxySync function. Shortly after the NGFS token contract deployment, the attacker manipulated the _uniswapV2Library variable to inflate their balance and swapped tokens for underlying assets.

Exploit Contract (on BNB Chain): 0xa608985f5b40cdf6862bec775207f84280a91e3a
Transaction Hash: 0x8ff764dde572928c353716358e271638fa05af54be69f043df72ad9ad054de25
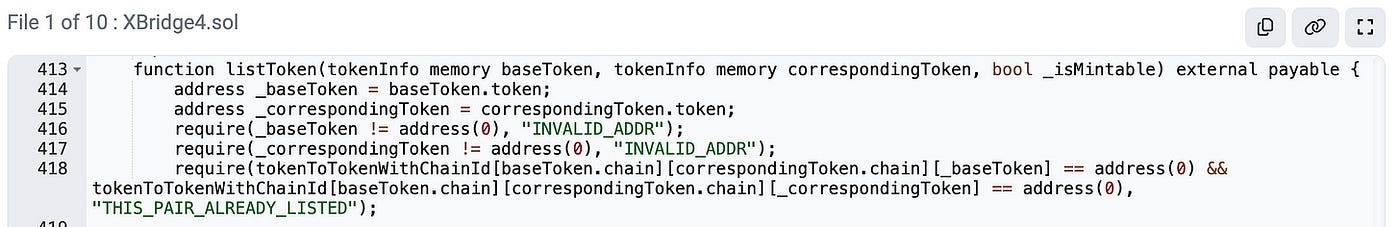
On April 24th, the XBridge exploit on the Ethereum Mainnet and the BNB chain resulted in a $1.4M loss. The root cause was a lack of regulated access control in the XBridge4 contract. The vulnerable contract allowed anyone to claim ownership of tokens via the listToken() function without verifying the token owner or caller. With ownership, the attacker extracted base tokens using the withdrawTokens() function. The XBridge team acknowledged the exploit.
Exploit Contract: 0x354CCA2F55ddE182d36fE34D673430E226a3cB8C
Transaction Hash: 0x903d88a92cbc0165a7f662305ac1bff97430dbcccaa0fe71e101e18aa9109c92
On April 24th, the YIEDL exploit on the BNB chain resulted in a $160K loss. The root cause was insufficient parameter validation in the SpotVault contract. The attacker first invoked the redeem() function with sharesToRedeem parameter as zero and then injected malicious payloads. This enabled arbitrary token exchanges and allowed redemptions without holding shares. The YIEDL team acknowledged the exploit and stated that their new BSC vault was deployed 17 hours before the exploit.
Exploit Contract (on BNB Chain): 0x4edda16ab4f4cc46b160abc42763ba63885862a4
Transaction Hash: 0x49ca5e188c538b4f2efb45552f13309cc0dd1f3592eee54decfc9da54620c2ec