
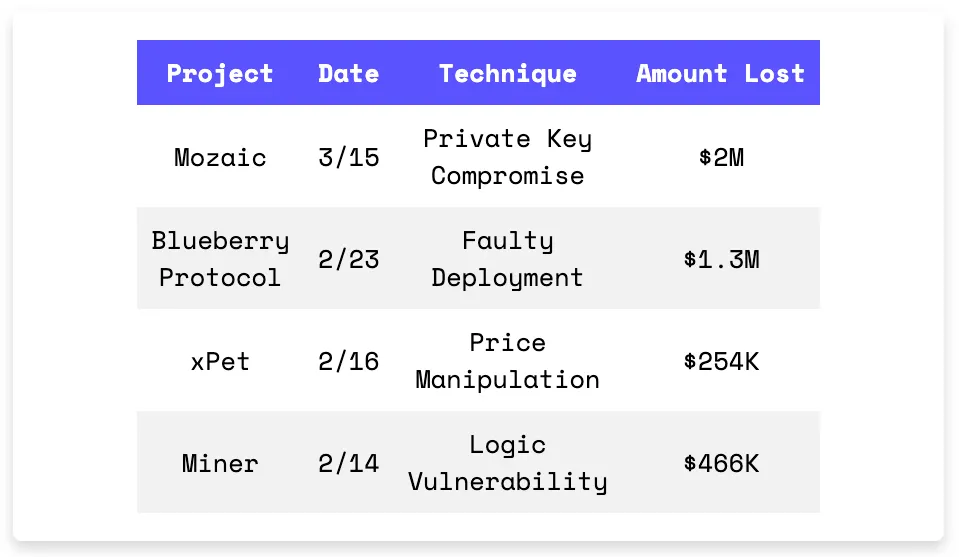
Mozaic lost $2M to an insider with stolen keys. Blueberry bled $1.3M after deploying a borrow contract using the wrong oracle decimals. xPet got hit for $254K via price manipulation in a PvP contract. Miner leaked $466K due to a cached balance logic flaw. Smart contract correctness doesn’t matter if your deployment, access control, or math assumptions are broken.
On March 15th, the Mozaic exploit on the Arbitrum chain resulted in a $2M loss. The root cause of the exploit was a compromise of Mozaic’s security module, which allowed the attacker to withdraw unauthorized funds. The Mozaic team stated that the exploiter was a Mozaic developer who had illegally obtained the private keys. Most of the stolen funds were transferred to MEXC and are frozen by the platform.
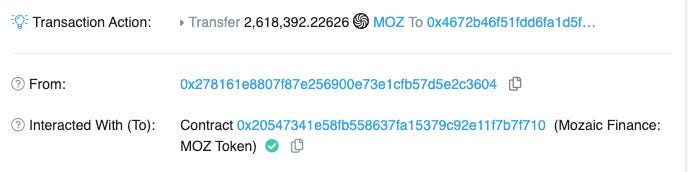
Exploit Contract (on Arbitrum chain): 0x20547341e58fb558637fa15379c92e11f7b7f710
Transaction Hash: 0xade7a4934db2c61beec8fe1cec506d7c643d894526dfccc8dff9d7bbe3d83404
On February 23rd, the Blueberry Protocol exploit on the Ethereum Mainnet resulted in a $1.3M loss. The root cause of the exploit was an unintended early deployment of the borrowing contract on February 22nd which used an incorrect price oracle. The incorrect oracle returned prices scaled to 18 decimals enabling the attacker to inflate the value of deposited assets with fewer than 18 decimals. The attacker made a profit by depositing 1WETH in the Blueberry Lending Market and borrowing 8,616 OHM, 913,262 USDC and 6.86 WBTC.
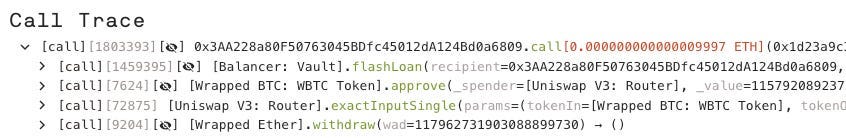
Exploit Contract: 0xE61ad5B0E40c856E6C193120Bd3fa28A432911B6
Transaction Hash: 0xf0464b01d962f714eee9d4392b2494524d0e10ce3eb3723873afd1346b8b06e4
On February 16th, the xPet exploit on the Arbitrum chain resulted in a $254K loss. The attacker deposited the funds into xPet’s PvP contract in three separate transactions, artificially inflating the BPET token’s price. The attacker then swapped all BPET tokens to get 91.5 ETH and made a profit. The xPet team acknowledged the incident and proposed a 10% bounty reward to the exploiter.
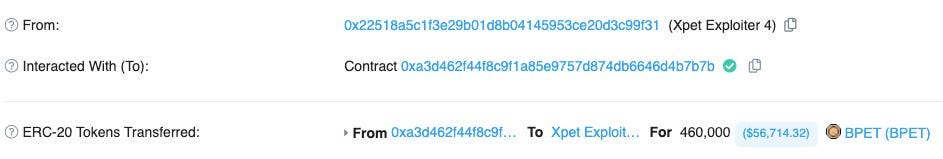
Exploit Contract (on Arbitrum chain): 0xA3d462f44F8C9F1a85e9757D874dB6646D4B7B7b
Transaction Hash: 0x1ad1f7536e2d91cc5aeef6e29f948ee73fa760a482b0455ca78adade83c4ef53
On February 14th, the Miner on the Ethereum Mainnet resulted in a $466K loss. The root cause of the exploit was a logic vulnerability in the private _update() function within the Miner’s contract. This function allowed users to double their balances when ‘from’ and ‘to’ addresses are the same, as the contract cached the toBalance value. The Miner team acknowledged the incident and offered a 30% bounty to the exploiter.
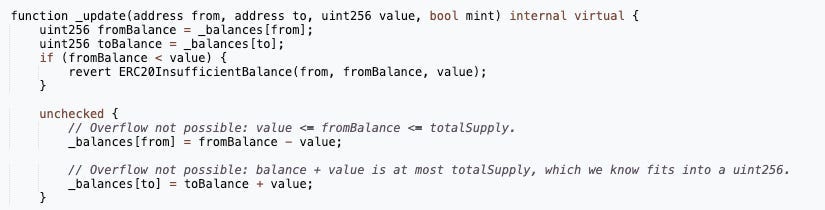
Exploit Contract: 0xe77ec1bf3a5c95bfe3be7bdbacfe3ac1c7e454cd
Transaction Hash: 0x4b9de8c56c8919e8598181449a3cc02df40435eb641eaec08ecce12d2342237f