
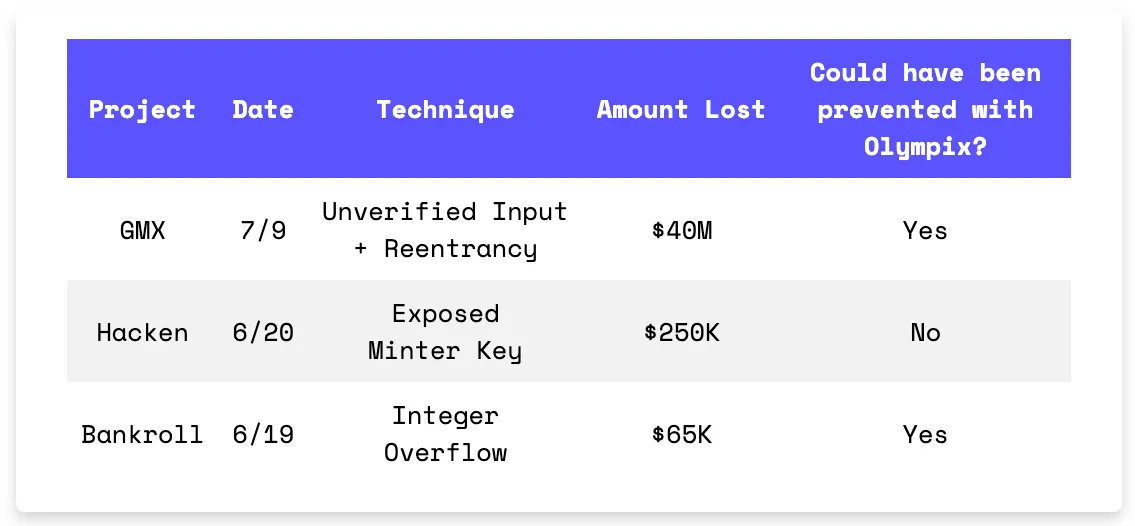
GMX lost $40M after allowing contract calls in a critical redemption function. Hacken saw $250K minted from a compromised key. Bankroll dropped $65K due to a classic integer underflow in outdated Solidity. Three different failure classes, one shared root: unchecked access where trust assumptions break.
On November 4th, the GMX exploit on Arbitrum resulted in a $40M loss. The root cause was that the executeDecreaseOrder() function accepted a smart contract as an input instead of an externally owned account (EOA). Unlike EOAs, smart contracts can execute arbitrary logic during callbacks. This allowed the attacker to reenter and manipulate internal state mid-transaction. If the function had restricted access to EOAs only, the reentrancy attack would not have been possible. The attacker opened a large short position to inflate the vault’s AUM, then redeemed GLP at the manipulated higher value to drain funds.


Exploited Contract (GMX: Order Book on Arbitrum): 0x09f77e8a13de9a35a7231028187e9fd5db8a2acb
Exploited Contract (GMX: Vault on Arbitrum): 0x489ee077994b6658eafa855c308275ead8097c4a
Transaction: 0x03182d3f0956a91c4e4c8f225bbc7975f9434fab042228c7acdc5ec9a32626ef
On June 21, the Hacken exploit on the Ethereum mainnet resulted in a $250K loss due a minter wallet key compromise. The attacker was able to mint HAI tokens and exchanged them for profit. Hacken team acknowledged the incident and confirmed that the deployer wallet and core infrastructure were not affected. Hacken has stopped minting and is improving its bridge architecture to prevent future risks.

Exploited Contract: 0x05fb86775fd5c16290f1e838f5caaa7342bd9a63
Transaction: 0xa0b32ee67d572df80a10c439d395a9907492d6ef62cbf53be66b3145cf479ab6
On June 19, the BankrollNetworkStack exploit on Ethereum and BNB chains resulted in a $65K loss. The root cause of the exploit was an integer underflow in the sell() function, where a signed integer was subtracted without safety checks: payoutsTo[_customerAddress] -= _updatedPayouts. The contract was compiled with Solidity 0.6.8, which lacks overflow/underflow protection. The attacker exploited this flaw to manipulate dividend accounting and withdraw more funds than allowed.

Exploited Contract (on BNB): 0xAdEfb902CaB716B8043c5231ae9A50b8b4eE7c4e
Transaction: 0x7226b3947c7e8651982e5bd777bca52d03ea31d19b515dec123595a4435ae22c