
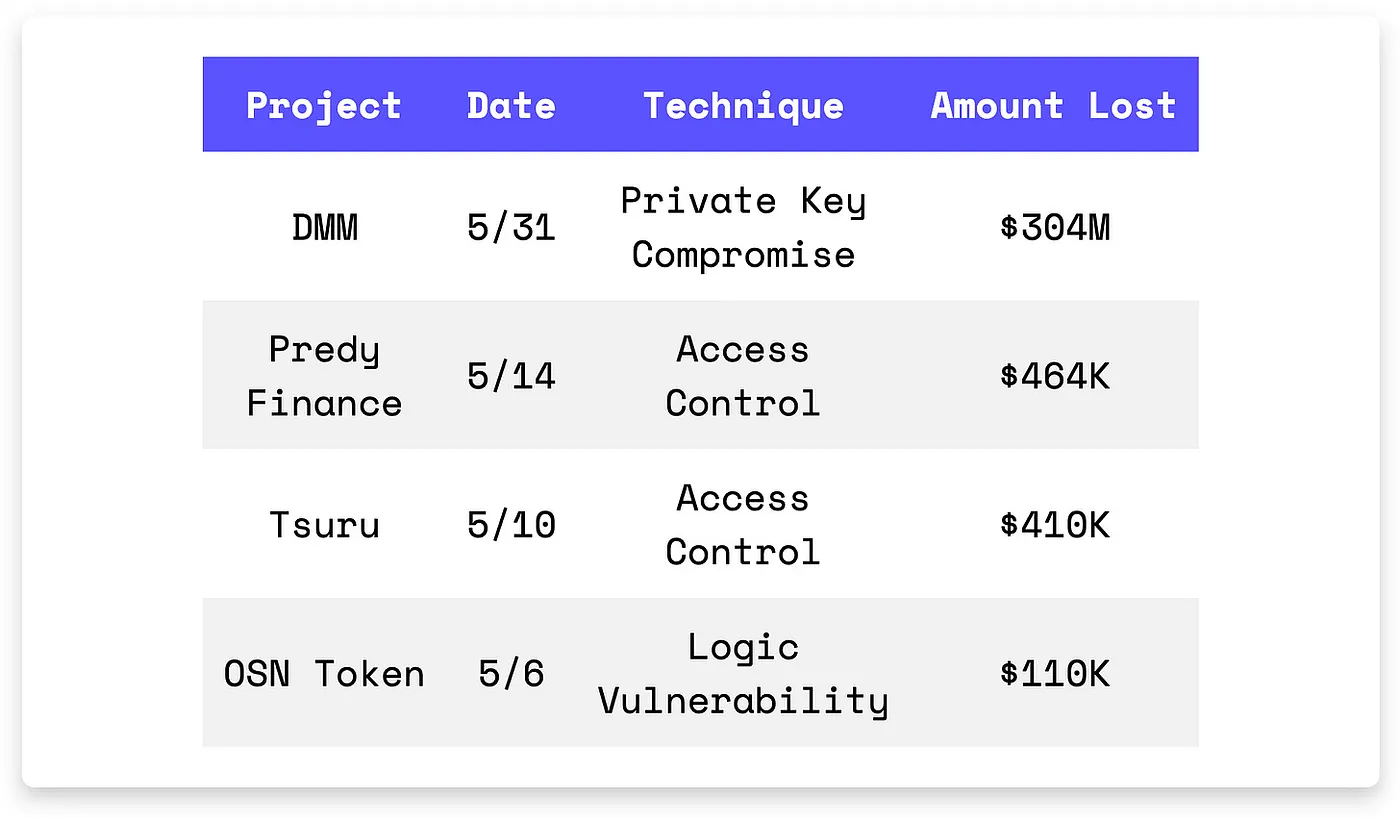
DMM lost $304M after a BTC wallet compromise. Predy Finance dropped $464K to a locker misuse in Uniswap callbacks. Tsuru’s weak token minting checks cost $410K. OSN leaked $110K through a dividend logic flaw. Largest heist of the year so far, all tied to stale access assumptions.
On May 31st, the DMM exploit resulted in a $304M loss. The root cause of the exploit was the compromise of DMM’s wallet, which allowed the attacker to withdraw 4,502.9 BTC. The DMM team acknowledged the incident and announced that they were investigating the issue and that they would reimburse all of the stolen assets to affected users. DMM spot purchases were also temporarily restricted.
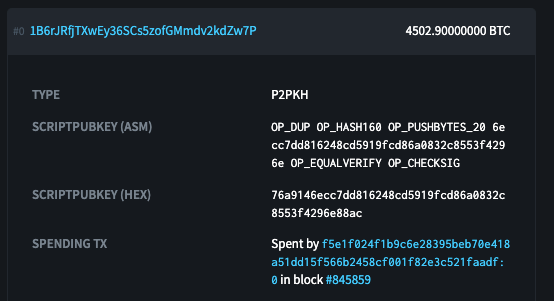
Exploit Address (BTC): 3P8MfdM4pULv7ozdQvfwAqNF29zAjmnUYD
Transaction Hash: 975ec405ac9dc9fa5ab8009d94d6a1fe31dff8a8127ea90d023104e52754e4d7
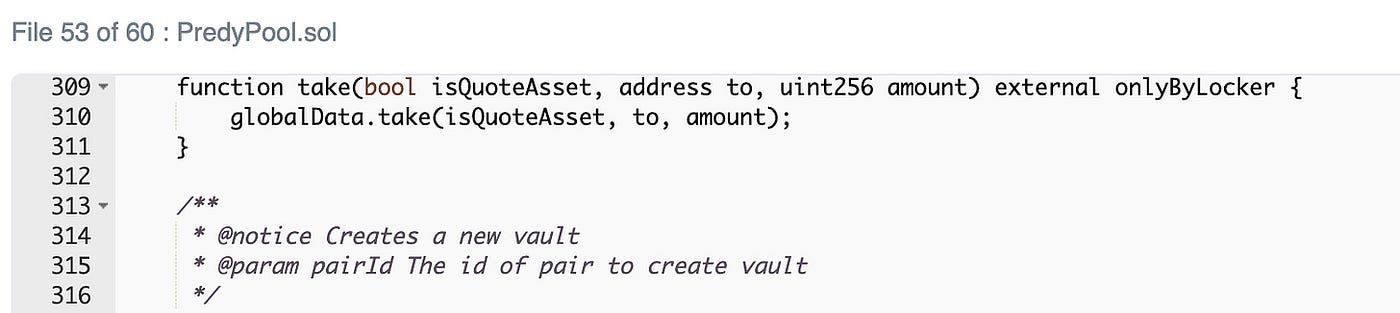
On May 14th, the Predy Finance exploit on the Arbitrum chain resulted in a loss of $464K. The root cause was a lack of regulated access control in PredyPool contract’s take() function, guarded by an onlyByLocker modifier, which was exploited due to improper validation in the trade() function. The attacker registered a Uniswap trading pair, manipulated the locker value, and used the callback function to transfer and withdraw tokens. The Predy Finance team acknowledged the exploit and proposed a 10% bounty to the exploiter.
Exploit Contract (on Arbitrum Chain): 0x7b8b944AB2f24C829504a7a6D70fce5298f2147c
Transaction Hash: 0xbe163f651d23f0c9e4d4a443c0cc163134a31a1c2761b60188adcfd33178f50f
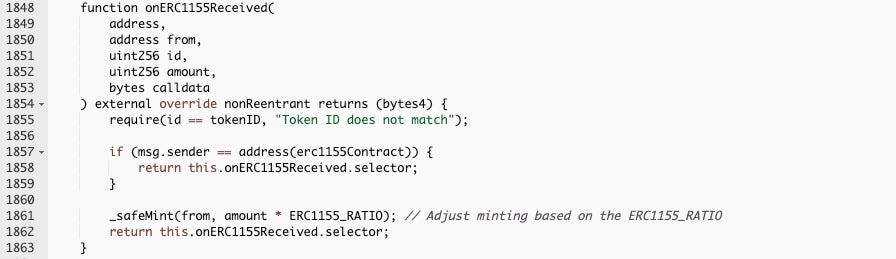
On May 10th, the Tsuru exploit on the Base chain resulted in a $410K loss. The root cause was a lack of regulated access control in the TSURUWrapper contract’s onERC1155Received() function, which lacked adequate authentication. This vulnerability allowed anyone to mint TSURU tokens and swap them for ETH on the Uniswap Liquidity pool. The attacker minted 167,200,200 TSURU tokens and swapped them for 137.78 ETH.
Exploit Contract (on Base Chain): 0x75ac62ea5d058a7f88f0c3a5f8f73195277c93da
Transaction Hash: 0xe63a8df8759f41937432cd34c590d85af61b3343cf438796c6ed2c8f5b906f62
On May 6th, the OSN token exploit on the BNB chain resulted in a $110K loss. The root cause was a logic flaw in the reward mechanism. The transfer() function of the OSN token contract invokes the swapAndSendDividends() function to sell tokens and send BUSD rewards to the OSNLpDividendTracker contract. The attacker repeatedly bought and sold OSN tokens by calling the swapAndSendDividends() function, causing the OSNLpDividendTracker contract to accumulate rewards.
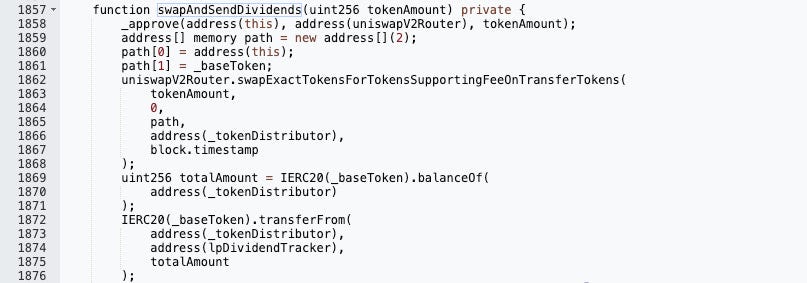
Exploit Contract (on BNB Chain): 0x810f4c6ae97bcc66da5ae6383cc31bd3670f6d13
Transaction Hash: 0xc7927a68464ebab1c0b1af58a5466da88f09ba9b30e6c255b46b1bc2e7d1bf0