
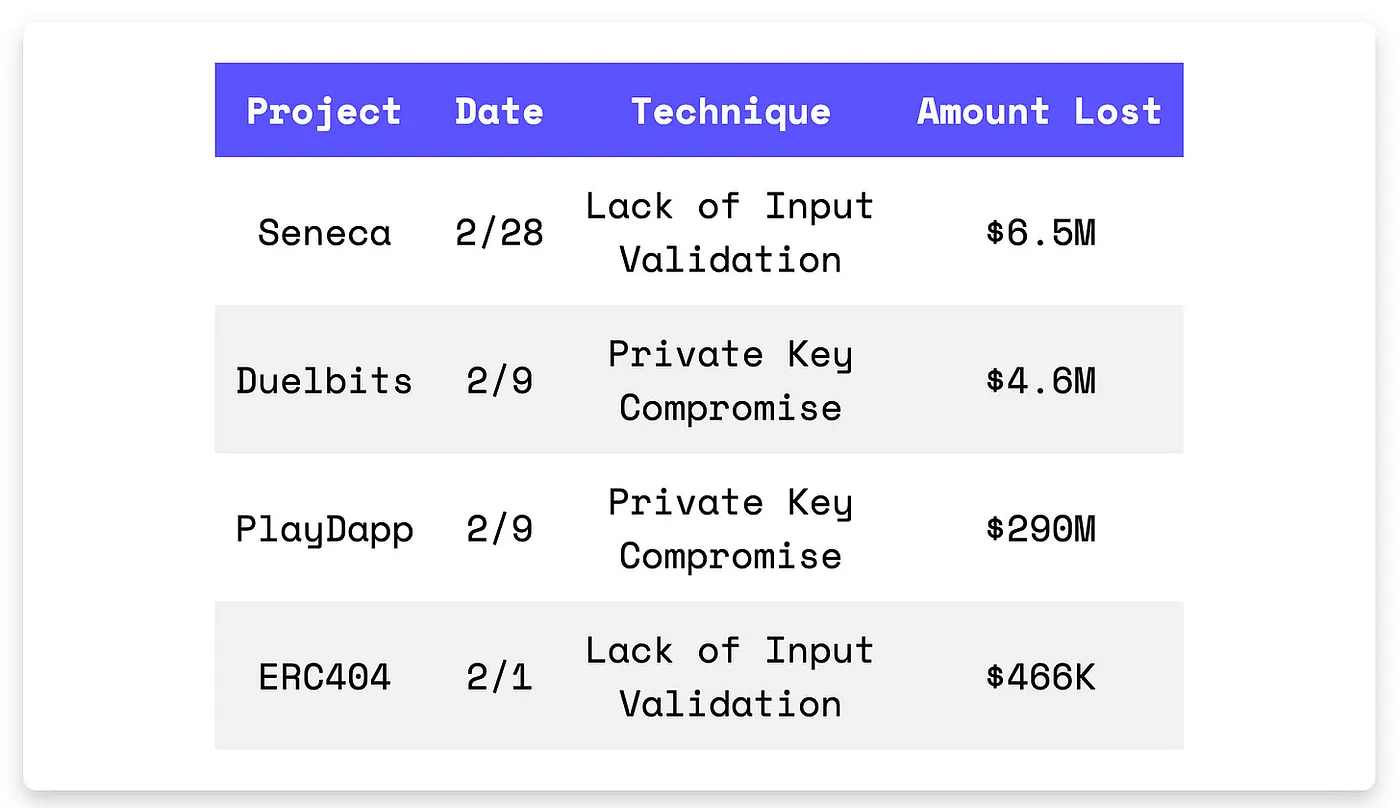
PlayDapp lost $290M after minter access was hijacked. Seneca bled $6.5M due to a logic flaw that allowed arbitrary calldata execution. Duelbits’ $4.6M loss stemmed from compromised hot wallet keys. ERC404 got drained for $466K after letting users trade NFTs without input validation. In all cases, privileged function misuse — not novel techniques — did the damage.
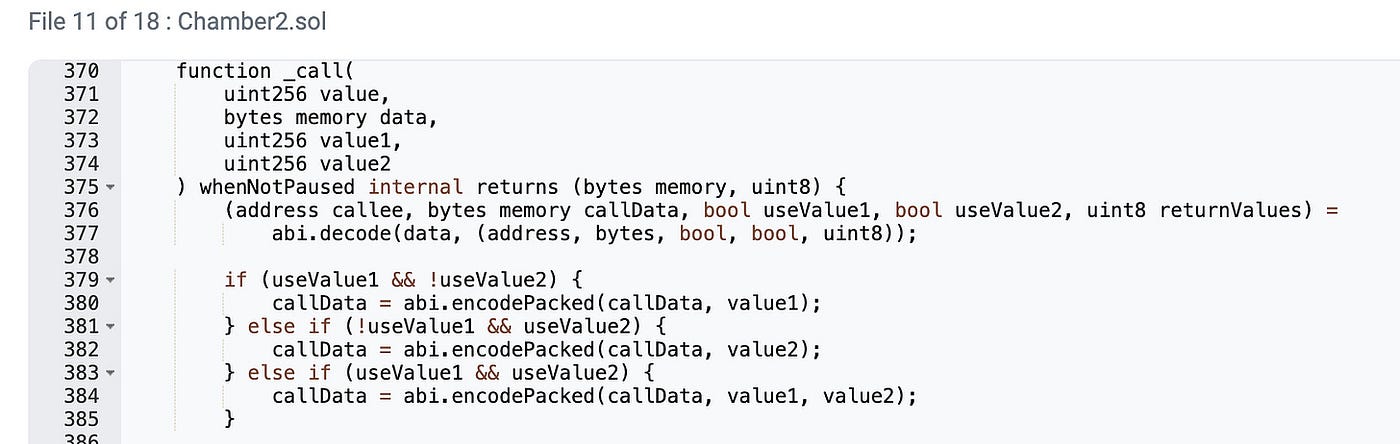
On February 28th, the Seneca exploit on the Ethereum Mainnet resulted in a $6.5M loss. The root cause of the hack was the absence of proper input validation in the private _call() function in Seneca’s Chamber2 contract. The flaw enabled the attacker to execute arbitrary calldata parameters, invoking the transferfrom() function and transferring approved tokens to their address. The Seneca team proposed a 20% bounty reward to the exploiter.
Exploit Contract: 0xbc83f2711d0749d7454e4a9d53d8594df0377c05
Transaction Hash: 0x9f3712672be7a120757d42fbe15ceefe9578914946bacbd0f3531e7fb7305576
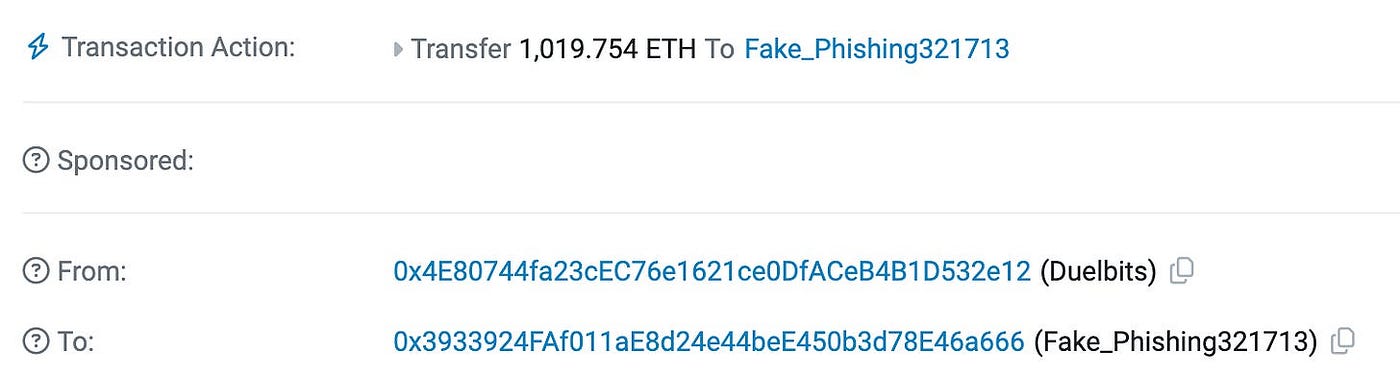
On February 9th, the Duelbits exploit on the Ethereum Mainnet resulted in a $4.6M loss. The root cause of the exploit was a compromise of Duelbits’ ETH hot wallet, which allowed the attacker to withdraw 1,700 ETH. The Duelbits team acknowledged the incident and confirmed that the customer funds and accounts are safe and secure. Duelbits services continue to operate without interruption.
Exploit Contract: 0x4e80744fa23cec76e1621ce0dfaceb4b1d532e12
Transaction Hash: 0x3bf414c5a62704cc917242336394eeeed15a7e1a50e857c15e611dab92999aa4
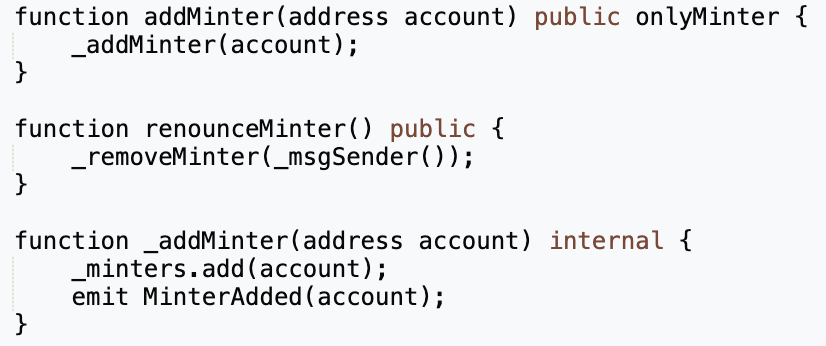
On February 9th, the PlayDapp exploit on the Ethereum Mainnet resulted in a $290M million loss. The root cause of the exploit was a compromise of PlayDapp’s private keys. The attacker was able to add a malicious contract address by calling the addMinter() function and mint unauthorized PLA tokens. The attacker repeated the minting transactions over four days.
Exploit Contract: 0x3a4f40631a4f906c2bad353ed06de7a5d3fcb430
Transaction Hash: 0xe8be05f6a3360f63b9e78a30b4ba16ea4c7d0b530a8abf99390f1c831851fb7e
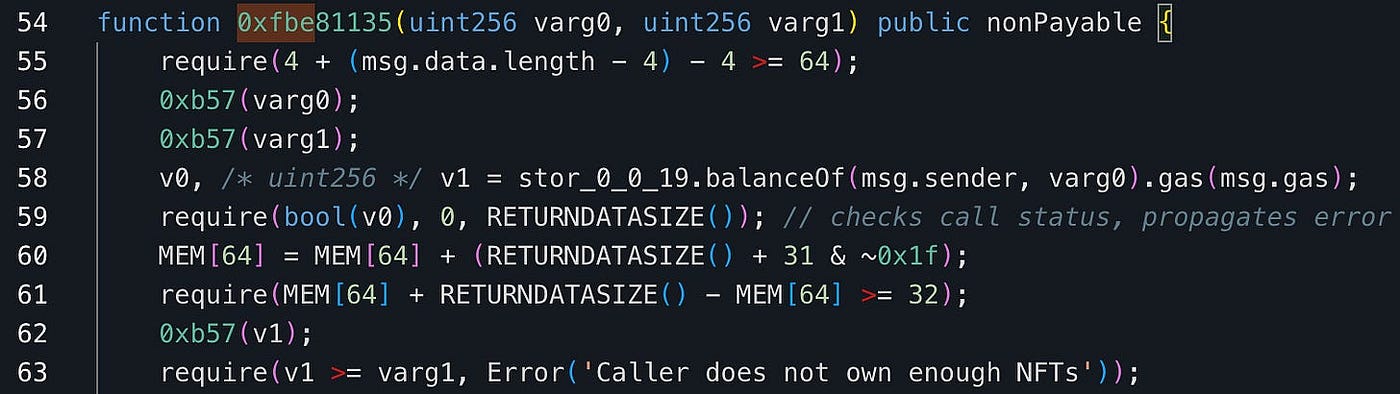
On February 1st, the ERC404 exploit on the Ethereum Mainnet resulted in a $466K loss. The root cause of the exploit was the lack of input validation in the function 0xfbe81135() that trades NFTs for tokens. By using zero “amount” arguments, varg0, and varg1 in a loop, the attacker received LOOGN tokens for free without giving back any NFTs.
Exploit Contract: 0x3559ee265fc9c5c9a333b07e0199480b4a84f369
Transaction Hash: 0xcc42f8d7ae3a45efeef7f6459d7d0250122b9536d3e5d37b5ec50b6db0bcdda2