
Jimbos' $7.5M Exploit Analyzed
In Brief:
- El Dorado Exchange’s Oracle contract got exploited.
- Jimbos Protocol lost $7.5M due to insufficient slippage control.
- CS Token price was manipulated using flash loans.
- Local Traders’ contract got exploited due to a lack of permission checks.
- Improper input validation resulted in an $87K loss for Sell Token.
Hacks:
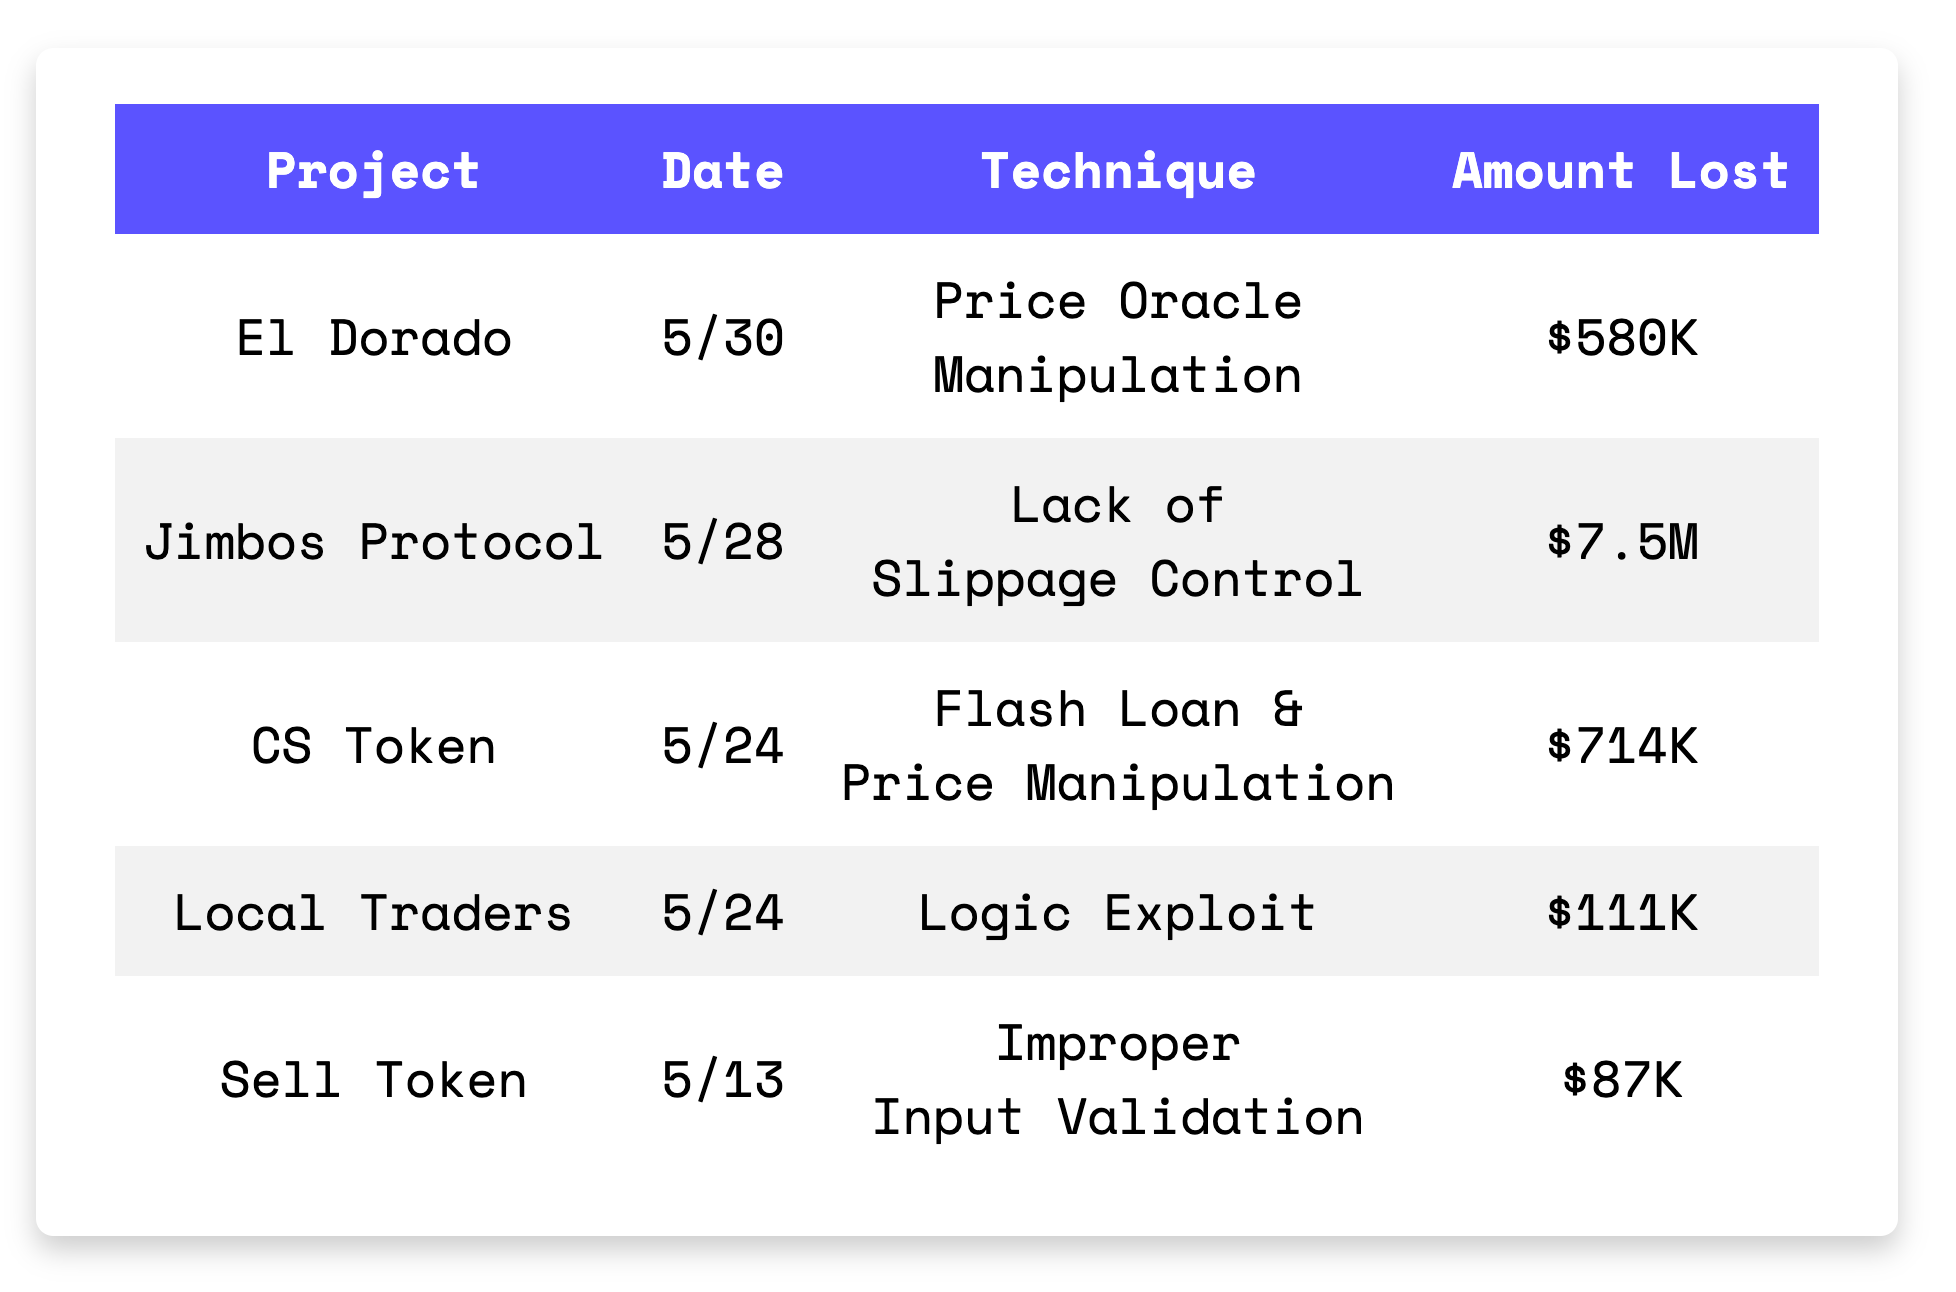
Hacks Analysis:
El Dorado Exchange | Amount Lost: $580K
On May 30, an exploit took place on the El Dorado Exchange (EDE) on the Arbitrum chain, resulting in a loss of $580K. The attack happened because the price oracle was manipulated. The attacker used the 0x147d9322() function in EDE's oracle contract to manipulate token prices. The attacker claimed to be a white hat and accused EDE of having a backdoor to manipulate the prices and steal user funds. EDE acknowledged the ability to manipulate prices but stated that it was intended to blacklist the exploiters. The attacker returned the funds and received a 10% bounty fee
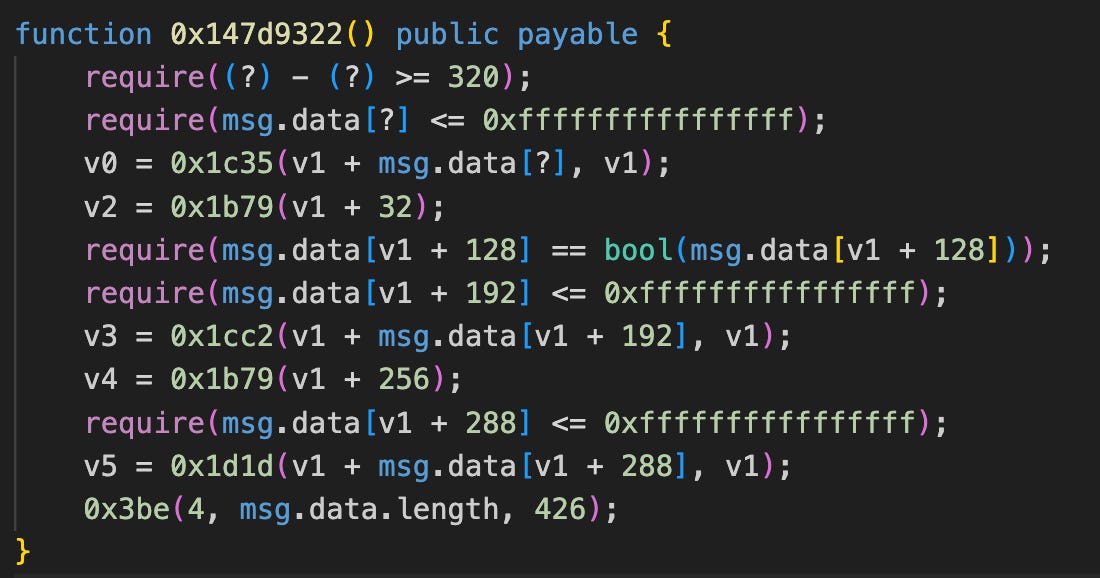
Decompiled Exploit Contract (on Arbitrum Chain): 0xD067e4B0144841bc79153874d385671Ea4c4e4DF
Transaction Hash: 0x72574fc0f85ed3c6fb78907fc938ce4d407817b1275bbd8b1ddc6de190550bf0
Jimbos Protocol | Amount Lost: $7.5M
On May 28, the Jimbos Protocol exploit on the Arbitrum chain resulted in a loss of $7.5M. The attack occurred because the JimbosController contract, responsible for balancing $JIMBO and WETH amounts by adding or removing liquidity, lacked a mechanism to prevent additions and removals during distorted token prices. The attacker used a flash loan to borrow WETH and swapped it for $JIMBO tokens. The attacker then transferred 100 $JIMBO tokens to the JimboController contract, which removed excess $JIMBO liquidity, increasing its price. Taking advantage of the inflated price, the attacker sold the overpriced $JIMBO tokens and profited from the exploit.
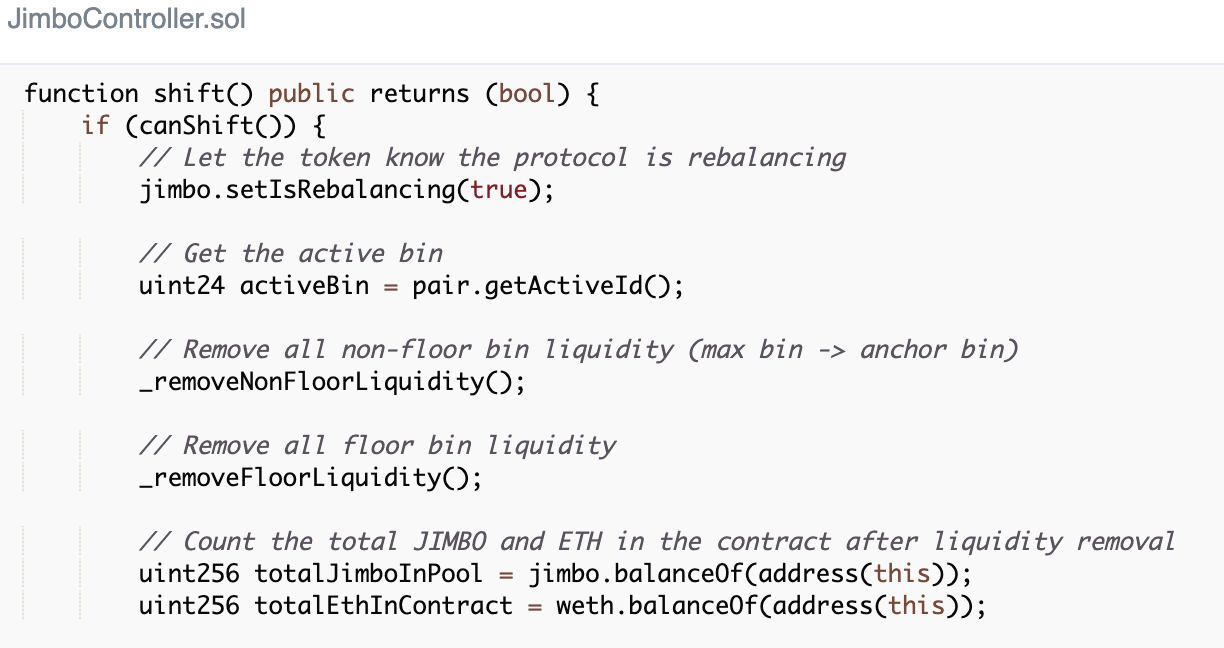
Exploit Contract (on Arbitrum Chain): 0x271944d9D8CA831F7c0dBCb20C4ee482376d6DE7
Transaction Hash: 0x44a0f5650a038ab522087c02f734b80e6c748afb207995e757ed67ca037a5eda
CS Token | Amount Lost: $714K
On May 24, the CS Token exploit on BNB chain resulted in a loss of $714K. The attacker manipulated the price of the $CS token by burning tokens, which reduced the token supply. The attacker used flash loans to borrow $80M worth of $BUSD from the PancakeSwap contract. Then, the attacker repeatedly exchanged $BUSD for $CS tokens using the CS contract. For each swap, the CS contract burned a portion of the tokens, gradually reducing the supply. This decreased supply increased the value of the $CS tokens, allowing the attacker to profit from the exploit.
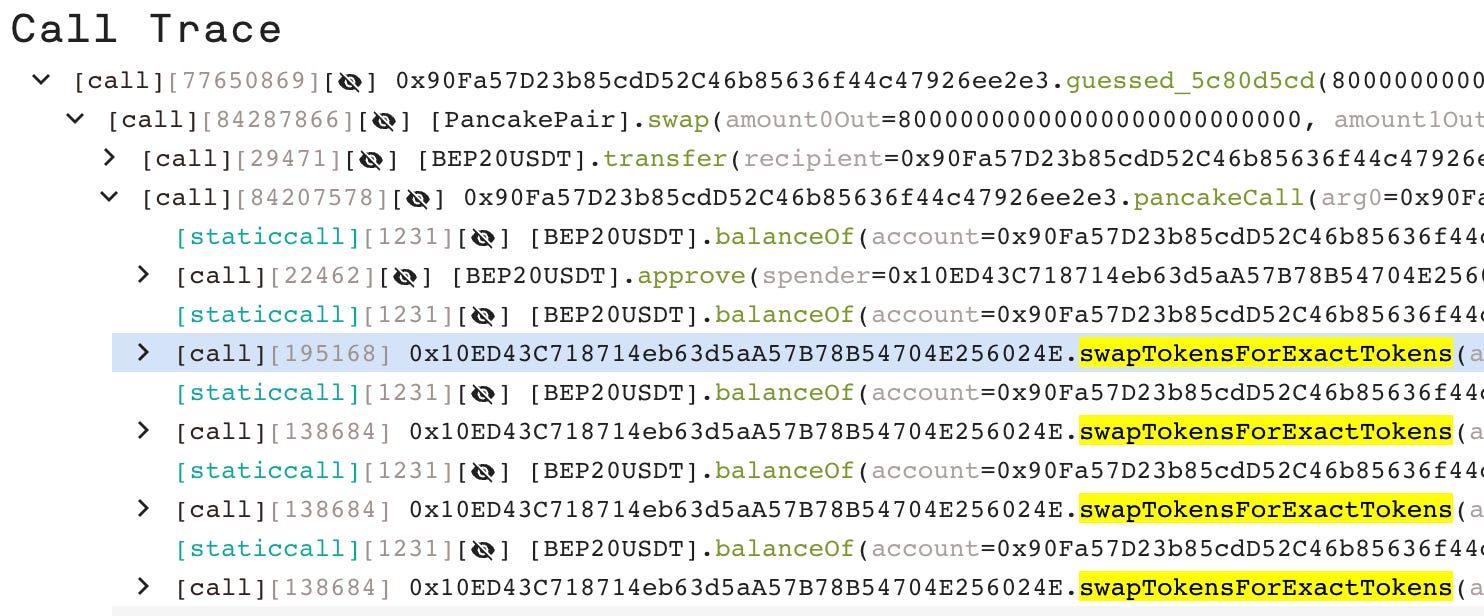
Exploit Contract (on BNB Chain): 0x8BC6Ce23E5e2c4f0A96429E3C9d482d74171215e
Transaction Hash: 0x906394b2ee093720955a7d55bff1666f6cf6239e46bea8af99d6352b9687baa4
Local Traders | Amount Lost: $111K
On May 23, the Local Traders Finance exploit on the BNB chain resulted in a loss of $111K. The attack occurred due to the absence of a permission check, which allowed the attacker to become the owner of the Local Traders' contract. Initially, the attacker set themselves as the contract owner. The attacker then triggered the private getTokenPrice() function and purchased $SLC tokens at an artificially low price. The getTokenPrice() function returned a low token price because the contract owner had previously manipulated the value of stor_3. The attacker then sold the $SLC tokens at the market rate and made a profit.

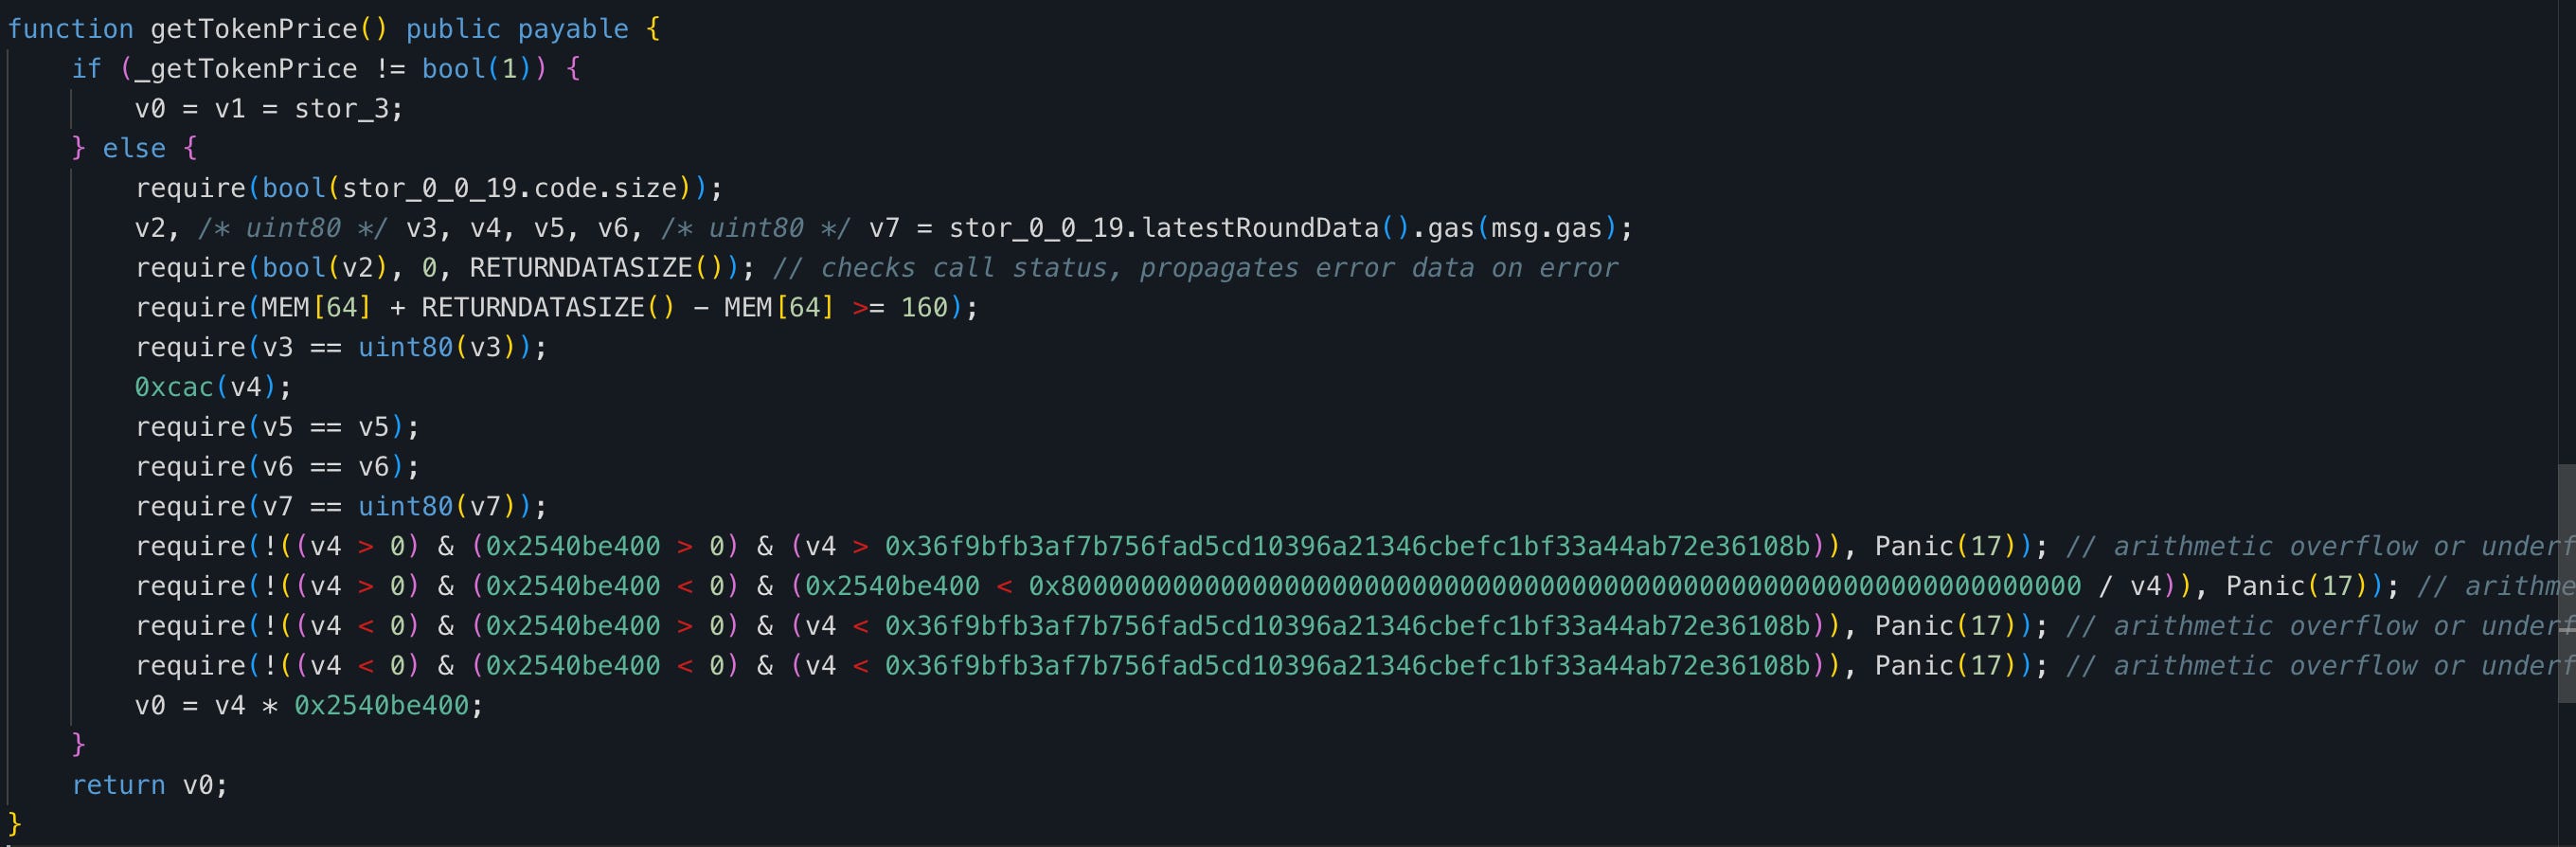
Decompiled Exploit Contract (on BNB Chain): 0x312DC37075646c7e0DBA21DF5BdFe69E76475fdc
Transaction Hash: 0x49a3038622bf6dc3672b1b7366382a2c513d713e06cb7c91ebb8e256ee300dfb
Sell Token | Amount Lost: $87K
On May 13, the Sell Token exploit on BNB chain resulted in a loss of $87K. The attack occurred due to improper input validation. The claim() function in Sell Token’s StakingRewards contract was missing input parameter checks. This vulnerability enabled the attacker to leverage a fake token named TokenA instead of USDT to collect $SELLC rewards. To prevent such attacks, the claim() function should have included input parameter validation to verify if TokenA was an authorized token. Subsequently, the attacker exchanged the accumulated $SELLC tokens for 408 WBNB on PancakeSwap.
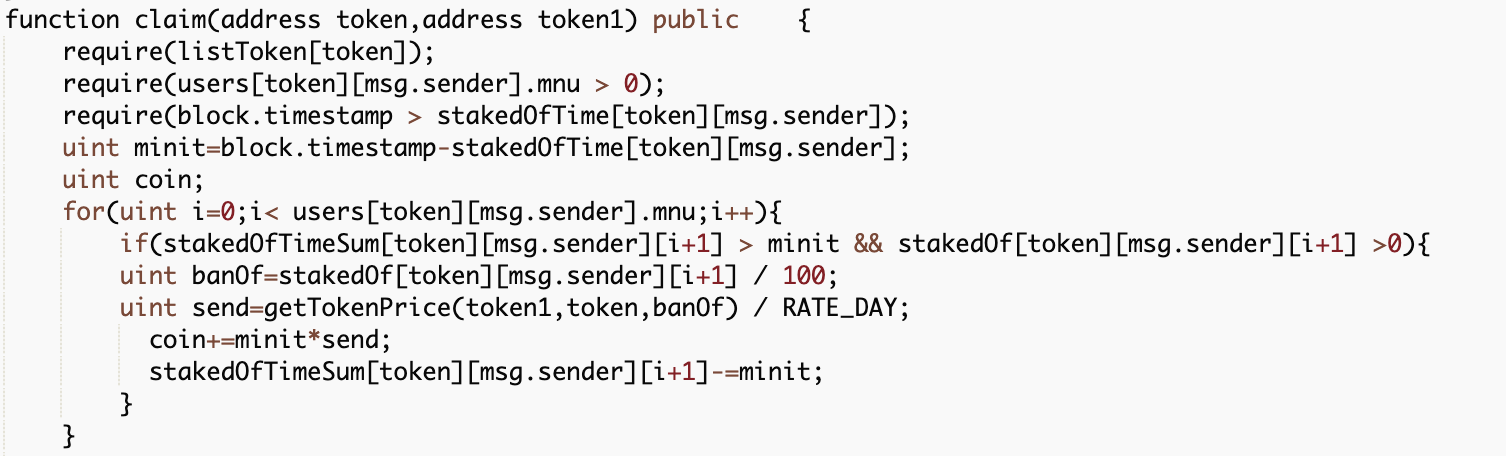
Exploit Contract (on BNB Chain): 0xeaF83465025b4Bf9020fdF9ea5fB6e71dC8a0779
Transaction Hash: 0xfe80df5d689137810df01e83b4bb51409f13c865e37b23059ecc6b3d32347136
More post-mortems
See every post-mortem →

See what Olympix finds on your own code
Send us a repo that's already been audited, and we'll run Olympix at the same commit and show you what comes back.